

FCSS_LED_AR-7.6認証試験の問題集解答を提供しています [2026年03月]
更新されたFCSS_LED_AR-7.6試験練習テスト問題
質問 # 54
Which encryption protocols can CAPWAP use to secure the data channel when communicating between a FortiGate wireless controller and FortiAP?
Response:
- A. SSL/TLS and IPsec
- B. SSH and SSL
- C. WPA3 and TLS
- D. DTLS and IPsec
正解:D
質問 # 55
An LDAP server has been successfully configured on FortiGate, which forwards authentication requests to a Windows Active Directory (AD) server. Users can authenticate using PAP, but authentication fails with MSCHAPv2. Why is it not recommended to use PAP for authentication?
Response:
- A. PAP does not support domain-based authentication for Active Directory.
- B. PAP requires the use of an insecure port that is easily blocked by firewalls.
- C. PAP sends passwords in cleartext.
- D. PAP is only supported for local user accounts, not external authentication sources.
正解:C
質問 # 56
Which command enables dynamic VLAN assignment under a FortiSwitch interface policy?
Response:
- A. set vlan-policy dynamic
- B. config switch-controller port-policy
- C. set dynamic-vlan enable
- D. set auth-mode radius
正解:A
質問 # 57
What are two requirements to enable digital certificate-based two-factor authentication on FortiAuthenticator?
(Choose two)
Response:
- A. Certificate Authority (CA) setup
- B. FortiAnalyzer integration
- C. Syslog server configuration
- D. Imported user certificates
正解:A、D
質問 # 58
To view FortiAP debug logs in the CLI, which command is used?
Response:
- A. execute wireless ap debug start
- B. debug controller-ap
- C. diagnose wireless-controller wlac -c
- D. diagnose debug enable → diagnose debug application cw_ac -1
正解:D
質問 # 59
Refer to the exhibits.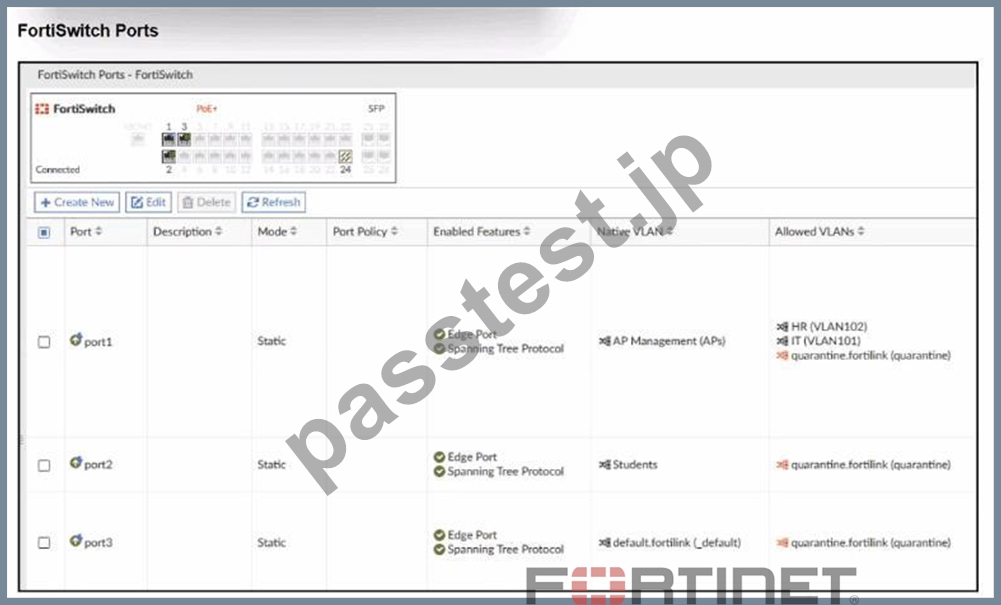

A NAC policy has been configured to apply traffic that flows through FortiSwitch port 2. Traffic that meets the NAC policy criteria will be assigned to the Students VLAN. However, the NAC policy does not seem to be taking effect.
Which configuration is missing?
- A. Port2 Access mode should be set to Port Policy mode.
- B. The MAC address or OS might be misconfigured for the connected device.
- C. The Students VLAN should be set to Allowed VLANs instead of Native VLAN.
- D. Port2 Access mode should be set to NAC mode.
正解:D
解説:
From the exhibits:
* FortiSwitch Ports viewshows:
* port2
* Mode: Static
* Native VLAN: Students
* Allowed VLANs: quarantine.fortilink (quarantine)
* NAC policy "Training":
* Switch FortiLink: fortilink
* Category:Device
* Matching criteria:
* MAC Address: 70:88:6b:8c:4b:0e (enabled)
* Operating System:Linux(enabled)
* Switch Controller Action:
* Assign VLAN = Students
* Bounce Port = enabled
Design intent:
Device with that MAC + OS Linux, when plugged intoport2, should be dynamically moved to VLAN Studentsby the NAC policy.
Why it doesn't work now
On FortiLink NAC,dynamic NAC decisions only apply on ports whose "Access Mode" is set to NAC:
* NAC mode = FortiGate controls theonboarding VLAN, evaluates NAC policies, and then dynamically reassigns the switch port VLAN (access, quarantine, etc.).
* Static mode(what we see on port2) means the port just uses its configurednative/allowed VLANs, and no NAC classificationhappens.
Right now:
* port2 is astatic access portwith Native VLAN = Students.
* The NAC policy exists, butFortiSwitch is not in NAC enforcement mode on that port, so the policy is never evaluated for traffic on port2.
Therefore, themissing configurationis:
Setport2toNAC mode(sometimes called "Access mode: NAC" or "NAC LAN edge port").
Once port2 is changed to NAC mode:
* Device initially lands in the onboarding/quarantine VLAN.
* FortiGate collects device info (MAC, OS, etc.).
* NAC policy "Training" matches MAC + Linux.
* Switch controller actionAssign VLAN = Studentsis applied.
* Port is bounced (if configured), bringing the device back up in VLAN Students.
Why the other options are wrong
* B. MAC or OS misconfigured
* Possible in general, but the question asks forwhich configuration is missing, and the exhibits clearly focus on port mode. Also, even with wrong MAC/OS, the port would still be in NAC mode; here NAC isn't even active.
* C. Port Policy mode
* Port policy (edge/trunk) is separate from NAC; NAC requires the specificNAC access mode.
* D. Students VLAN should be Allowed VLANs instead of Native VLAN
* For an access port, having Students as thenative VLANis correct. NAC policy's Assign VLAN will set that as access VLAN; no need to make it an allowed trunk VLAN.
質問 # 60
Which authentication method can be used on FortiAuthenticator to implement certificate-based authentication?
Response:
- A. LDAP authentication
- B. RADIUS only
- C. PAP
- D. EAP-TLS
正解:D
質問 # 61
Which steps are required to configure RADIUS SSO (RSSO) on FortiAuthenticator?
(Choose three)
Response:
- A. Enable RSSO in FortiGate security policy
- B. Set FortiAuthenticator as LDAP proxy
- C. Configure FortiGate to use FortiAuthenticator as RADIUS server
- D. Define RSSO attribute in FortiAuthenticator
- E. Enable RSSO group mapping
正解:C、D、E
質問 # 62
What are the advantages of dynamic VLAN assignment in LAN edge designs?
(Choose two)
Response:
- A. Disables STP on access ports
- B. Hard-codes VLANs to interfaces
- C. Reduces configuration effort for mobile users
- D. Improves scalability and policy enforcement
正解:C、D
質問 # 63
In a FortiNAC deployment, what does the term "dissolvable agent" refer to?
Response:
- A. A configuration template
- B. A cloud-based identity system
- C. An endpoint license
- D. A temporary agent downloaded for posture checks
正解:D
質問 # 64
Which VLAN is used by FortiGate to place devices that fail to match any configured NAC policies? CRSPAN
- A. NAC
- B. Onboarding
- C. segment
- D. Quarantine
正解:B
解説:
In FortiLink NAC for LAN Edge:
* When a device first connects, it is placed into theonboarding VLAN.
* NAC policies then classify the device (by MAC, OS, user, EMS tag, etc.).
* If a NAC policy matches, the device may be moved to anaccess VLANorquarantine VLAN.
* Ifno NAC policy matches, the device simplystays in the onboarding VLAN.
FortiOS / LAN Edge documentation describes the onboarding VLAN as thedefault VLAN for unknown or unclassified devices, until NAC policy evaluation moves them elsewhere.
質問 # 65
What logs or tools can be used to troubleshoot wireless AP communication issues in FortiGate?
(Choose two)
Response:
- A. Event Logs > WiFi Events
- B. VLAN trunk statistics
- C. CAPWAP logs
- D. Application control profiles
正解:A、C
質問 # 66 
You've configured the FortiLink interface, and the DHCP server is enabled by default. The resulting DHCP server settings are shown in the exhibit. What is the role of the vci-string setting in this configuration?
- A. To ignore DHCP requests coming from FortiSwitch and FortiExtender devices.
- B. To connect, devices must match the VCI string; otherwise, they will not receive an IP address.
- C. To reserve IP addresses for FortiSwitch and FortiExtender devices.
- D. To restrict the IP address assignment to devices that have FortiSwitch or FortiExtender as their hostname.
正解:B
解説:
The DHCP configuration shows:
set vci-match enable
set vci-string "FortiSwitch" "FortiExtender"
What this means
VCI = Vendor Class Identifier (DHCP option 60)
When vci-match is enabled, the DHCP server will only respond to DHCP requests from clients whose VCI string matches the configured vendor identifiers.
FortiSwitch and FortiExtender both send DHCP option 60 with:
"FortiSwitch"
"FortiExtender"
This is used in FortiLink deployments so only these devices receive IP addresses on the FortiLink network.
Therefore:
C). To connect, devices must match the VCI string; otherwise, they will not receive an IP address.
#Correct.
This perfectly matches FortiGate FortiLink DHCP behavior.
Summary of incorrect options
A - Ignore FortiSwitch/FortiExtender
#Opposite behavior.
B - Restrict based on hostname
#VCI does NOT check hostname.
D - Reserve IPs
#No reservation occurs; it's filtering, not reserving.
質問 # 67
What must be done on the FortiGate to fully enable RSSO with FortiAuthenticator?
Response:
- A. Enable RSSO on user group
- B. Disable RSSO attribute
- C. Set RADIUS client IP
- D. Add syslog filter
正解:A
質問 # 68
Refer to the exhibits which show the FortiSwitch and FortiGate interface configurations.
FortiSwitch VLAN configuration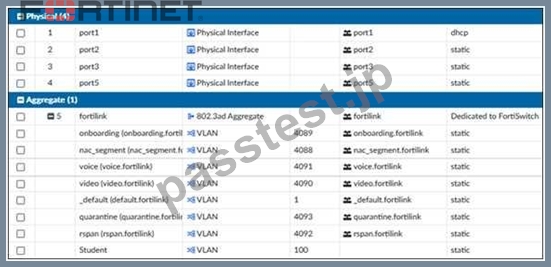
Port2 interface configuration
Which two statements describe how port2 handles tagged and untagged traffic? (Choose two.) Response:
- A. Port2 accepts ingress tagged traffic for VLAN IDs 4091 and 4093 only.
- B. Port2 assigns ingress untagged traffic to VLAN 100.
- C. Port2 tags egress traffic for VLAN 100.
- D. Port2 accepts ingress untagged traffic for VLAN IDs 100, 4091, and 4093 only.
正解:A、B
質問 # 69
A network administrator wants a newly deployed FortiGate to automatically discover its FortiManager without manual configuration. Which of the following must be correctly configured for this process to work?
Response:
- A. FortiGate interface administrative access must have enabled Security Fabric Connection.
- B. The FortiGate interface must be set to receive an IP address over DHCP.
- C. The DHCP server must include Option 240 or Option 241 in its lease offers.
- D. The DHCP server must provide a valid default gateway to reach FortiManager.
正解:C
質問 # 70
Which Fortinet technologies can dynamically assign VLANs based on user or device attributes?
(Choose two)
Response:
- A. FortiLink NAC
- B. FortiAnalyzer
- C. FortiAuthenticator
- D. FortiCloud
正解:A、C
質問 # 71
Which field in a RADIUS accounting message is used by FortiAuthenticator for RSSO group assignment?
Response:
- A. User-Password
- B. NAS-Identifier
- C. Calling-Station-ID
- D. Filter-ID
正解:D
質問 # 72
......
検証済みのFCSS_LED_AR-7.6問題集と解答を使って100%一発合格保証で更新された問題集:https://drive.google.com/open?id=1SC1AXI8OVfob5woQAZxEDTRmmaXi8ncW
合格させるFortinet Certified Solution Specialist FCSS_LED_AR-7.6試験には127問があります:https://www.passtest.jp/Fortinet/FCSS_LED_AR-7.6-shiken.html