
試験名称: Certified Kubernetes Security Specialist (CKS)
認証ベンダー: Linux Foundation
対応認証: Kubernetes Security Specialist

オーバー 46460+ 人満足している顧客
CKS ソフト版
- インストール可能なソフトウェア応用
- 本番の試験環境をシミュレート
- 人にCKS試験の自信をもたせる
- MSシステムをサポート
- 練習用の2つモード
- いつでもオフラインで練習
- ソフト版キャプチャーをチェックする
- 問題と解答: 66
- 最近更新時間: 2026-11-02
- 価格: ¥7500
CKS オンライン版
- 学習を簡単に、便利オンラインツール
- インスタントオンラインアクセス
- すべてのWebブラウザをサポート
- いつでもオンラインで練習
- テスト履歴と性能レビュー
- Windows/Mac/Android/iOSなどをサポート
- オンラインテストエンジンを試用する
- 問題と解答: 66
- 最近更新時間: 2026-11-02
- 価格: ¥7500
CKS PDF版
- 印刷可能なCKS PDF版
- Linux Foundation専門家による準備
- インスタントダウンロード
- いつでもどこでも勉強
- 365日無料アップデート
- CKS無料PDFデモをご利用
- PDF版試用をダウンロードする
- 問題と解答: 66
- 最近更新時間: 2026-11-02
- 価格: ¥7500
最も有効な CKS 試験参考書

インスタントダウンロード: 支払いが完了すると、システムから購入した商品がメールで自動的にメールボックスに送信されます。 (12時間以内に受信されない場合は、ご連絡ください。注意:スパムを確認することを忘れないでください)。
100%返金保証
PassTestは、顧客の間で初めて合格率99.6%を達成しています。  弊社は製品に自信を持っており、面倒な製品を提供していません。
- 高品質試験問題集参考書
- 三つバージョンは選択可能
- 十年の優位性
- 365日無料アップデット
- いつでもどこで勉強
- 100%安全なショッピング体験
言語がわかりやすい
業界の新人として、プロの本の中で読めない言葉や表現は怒りを感じさせることがよくありますが、CKS練習教材はこの問題を完全に解決するのに役立ちます。教材に雇われた業界の専門家は理解しにくいすべての専門用語を説明します。例えば、図表などです。CKS実際のテストで使用されるすべての言語は、非常に簡単に理解しやすいものでした。私たちの教材を使えば、専門書の内容を理解できないことを心配する必要はありません。また、個別指導クラスに行くために高価な授業料を費やす必要はありません。CKSテストエンジンは研究のすべての問題を解決するのを助けることができます。
Linux Foundation CKS 認定試験の出題範囲:
| トピック | 出題範囲 |
|---|---|
| トピック 1 |
|
| トピック 2 |
|
| トピック 3 |
|
参照:https://training.linuxfoundation.org/certification/certified-kubernetes-security-specialist/#exams
CKS練習問題は学生に適用されるだけでなく、サラリーマンと職場の退役軍人にも適用されます。私たちの学習教材は、すべての人が学び理解することができるようにするために、非常に勉強しやすいです。CKS実際のテストはまたお客様が教科書の読書の煩わしさを避けることができます。その上練習問題をする過程ですべての重要な知識を習得させます。CKSテストエンジンを選択した理由は以下の通りです。
100%合格率保証
教材の内容を順守し、毎日勉強し、定期的に自己試験を受けていれば、CKS模擬教材を購入したすべての学生がプロの資格試験に合格することができるはずです。不幸にして私達のCKS実際のテストに失敗したら、我々はお客様に全額払戻しを提供します、そして払い戻しプロセスは非常に簡単です。成績証明書を弊社のスタッフに提供する限り、すぐに払い戻しを受けます。もちろん、購入する前に、弊社の学習教材で無料のトライアルサービスを提供しています。ウェブサイトにログインしている限り、無料でトライアル質問バンクをダウンロードできます。CKSテストエンジンを試した後、お客様はそれらを気に入るはずと信じています。
時間を節約し効率的な学習方法
私たちのCKS練習教材には3つの異なるバージョンがあります:PDF、ソフトウェアおよびオンラインのAPP。この3つのバージョンは異なる研究グループが彼らの研究方法を選択する可能性を提供します。サラリーマンであれば、地下鉄やバスでCKSの実際のテストのオンライン版を学ぶことができます。学生であれば、食事のために並んでいるときあなたはそれを検討することができます。主婦であれば、子供が眠っているときに勉強することができます。同時に、私たちの教材はオフライン学習をサポートしています。これはネットワークなしでは学ぶ方法がないという事態を回避します。同時に、CKSテストエンジンを使用して検索することで、タイトルからナレッジポイントを検索できます。ナレッジポイントをもっと深く覚えておくことができるだけでなく、本を読むという煩わしい プロセスを回避することもできます。
Linux Foundation Certified Kubernetes Security Specialist (CKS) 認定 CKS 試験問題:
SIMULATION
You must complete this task on the following cluster/nodes:
Cluster: trace
Master node: master
Worker node: worker1
You can switch the cluster/configuration context using the following command:
[desk@cli] $ kubectl config use-context trace
Given: You may use Sysdig or Falco documentation.
Task:
Use detection tools to detect anomalies like processes spawning and executing something weird frequently in the single container belonging to Pod tomcat.
Two tools are available to use:
1. falco
2. sysdig
Tools are pre-installed on the worker1 node only.
Analyse the container's behaviour for at least 40 seconds, using filters that detect newly spawning and executing processes.
Store an incident file at /home/cert_masters/report, in the following format:
[timestamp],[uid],[processName]
Note: Make sure to store incident file on the cluster's worker node, don't move it to master node.
正解:
See the Explanation below
Explanation:
$vim /etc/falco/falco_rules.local.yaml
- rule: Container Drift Detected (open+create)
desc: New executable created in a container due to open+create
condition: >
evt.type in (open,openat,creat) and
evt.is_open_exec=true and
container and
not runc_writing_exec_fifo and
not runc_writing_var_lib_docker and
not user_known_container_drift_activities and
evt.rawres>=0
output: >
%evt.time,%user.uid,%proc.name # Add this/Refer falco documentation
priority: ERROR
$kill -1 <PID of falco>
Explanation:
[desk@cli] $ ssh node01
[node01@cli] $ vim /etc/falco/falco_rules.yaml
search for Container Drift Detected & paste in falco_rules.local.yaml
[node01@cli] $ vim /etc/falco/falco_rules.local.yaml
- rule: Container Drift Detected (open+create)
desc: New executable created in a container due to open+create
condition: >
evt.type in (open,openat,creat) and
evt.is_open_exec=true and
container and
not runc_writing_exec_fifo and
not runc_writing_var_lib_docker and
not user_known_container_drift_activities and
evt.rawres>=0
output: >
%evt.time,%user.uid,%proc.name # Add this/Refer falco documentation
priority: ERROR
[node01@cli] $ vim /etc/falco/falco.yaml
SIMULATION
Context
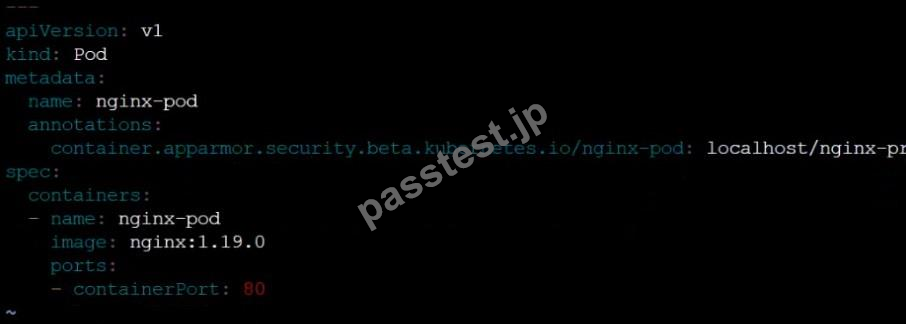
AppArmor is enabled on the cluster's worker node. An AppArmor profile is prepared, but not enforced yet.
Task
On the cluster's worker node, enforce the prepared AppArmor profile located at /etc/apparmor.d/nginx_apparmor.
Edit the prepared manifest file located at /home/candidate/KSSH00401/nginx-pod.yaml to apply the AppArmor profile.
Finally, apply the manifest file and create the Pod specified in it.
正解:
See the Explanation belowExplanation:

SIMULATION
Context
For testing purposes, the kubeadm provisioned cluster 's API server
was configured to allow unauthenticated and unauthorized access.
Task
First, secure the cluster 's API server configuring it as follows:
. Forbid anonymous authentication
. Use authorization mode Node,RBAC
. Use admission controller NodeRestriction
The cluster uses the Docker Engine as its container runtime . If needed, use the docker command to troubleshoot running containers.
kubectl is configured to use unauthenticated and unauthorized access. You do not have to change it, but be aware that kubectl will stop working once you have secured the cluster .
You can use the cluster 's original kubectl configuration file located at etc/kubernetes/admin.conf to access the secured cluster.
Next, to clean up, remove the ClusterRoleBinding
system:anonymous.
正解:
See the Explanation below for complete solution
Explanation:
1) SSH to control-plane node
ssh cks000002
sudo -i
2) Edit API Server static pod manifest
API server in kubeadm runs as a static pod.
vi /etc/kubernetes/manifests/kube-apiserver.yaml
3) Apply required API Server security settings
3.1 Forbid anonymous authentication
Find command: section and ensure this line exists:
- --anonymous-auth=false
3.2 Use authorization mode Node,RBAC
Ensure exactly this line exists (and no AlwaysAllow):
- --authorization-mode=Node,RBAC
❌ Remove if present:
- --authorization-mode=AlwaysAllow
3.3 Enable admission controller NodeRestriction
Find --enable-admission-plugins and ensure NodeRestriction is included.
Correct example:
- --enable-admission-plugins=NodeRestriction
If other plugins already exist, append NodeRestriction, e.g.:
- --enable-admission-plugins=NamespaceLifecycle,ServiceAccount,NodeRestriction
4) Save file and let kubelet restart API server
Just save and exit (:wq)
Kubelet will automatically restart the API server pod.
5) Switch kubectl to secured config
Current kubectl will stop working after API server hardening.
export KUBECONFIG=/etc/kubernetes/admin.conf
Verify access:
kubectl get nodes
6) Remove insecure ClusterRoleBinding
Delete system:anonymous binding:
kubectl delete clusterrolebinding system:anonymous
Verify removal:
kubectl get clusterrolebinding | grep anonymous
(no output = correct)
7) Quick validation (optional but fast)
API server flags check:
grep -n "anonymous-auth" /etc/kubernetes/manifests/kube-apiserver.yaml
grep -n "authorization-mode" /etc/kubernetes/manifests/kube-apiserver.yaml grep -n "NodeRestriction" /etc/kubernetes/manifests/kube-apiserver.yaml
SIMULATION
Context:
Cluster: gvisor
Master node: master1
Worker node: worker1
You can switch the cluster/configuration context using the following command:
[desk@cli] $ kubectl config use-context gvisor
Context: This cluster has been prepared to support runtime handler, runsc as well as traditional one.
Task:
Create a RuntimeClass named not-trusted using the prepared runtime handler names runsc.
Update all Pods in the namespace server to run on newruntime.
正解:
See the Explanation below
Explanation: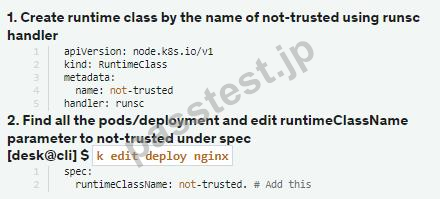
Explanation:
[desk@cli] $vim runtime.yaml
apiVersion: node.k8s.io/v1
kind: RuntimeClass
metadata:
name: not-trusted
handler: runsc
[desk@cli] $ k apply -f runtime.yaml
[desk@cli] $ k get pods
NAME READY STATUS RESTARTS AGE
nginx-6798fc88e8-chp6r 1/1 Running 0 11m
nginx-6798fc88e8-fs53n 1/1 Running 0 11m
nginx-6798fc88e8-ndved 1/1 Running 0 11m
[desk@cli] $ k get deploy
NAME READY UP-TO-DATE AVAILABLE AGE
nginx 3/3 11 3 5m
[desk@cli] $ k edit deploy nginx
SIMULATION
Service is running on port 389 inside the system, find the process-id of the process, and stores the names of all the open-files inside the /candidate/KH77539/files.txt, and also delete the binary.
正解:
See the Explanation belowExplanation:
root# netstat -ltnup
Active Internet connections (only servers)
Proto Recv-Q Send-Q Local Address Foreign Address State PID/Program name tcp 0 0 127.0.0.1:17600 0.0.0.0:* LISTEN 1293/dropbox tcp 0 0 127.0.0.1:17603 0.0.0.0:* LISTEN 1293/dropbox tcp 0 0 0.0.0.0:22 0.0.0.0:* LISTEN 575/sshd tcp 0 0 127.0.0.1:9393 0.0.0.0:* LISTEN 900/perl tcp 0 0 :::80 :::* LISTEN 9583/docker-proxy tcp 0 0 :::443 :::* LISTEN 9571/docker-proxy udp 0 0 0.0.0.0:68 0.0.0.0:* 8822/dhcpcd
...
root# netstat -ltnup | grep ':22'
tcp 0 0 0.0.0.0:22 0.0.0.0:* LISTEN 575/sshd
The ss command is the replacement of the netstat command.
Now let's see how to use the ss command to see which process is listening on port 22:
root# ss -ltnup 'sport = :22'
Netid State Recv-Q Send-Q Local Address:Port Peer Address:Port
tcp LISTEN 0 128 0.0.0.0:22 0.0.0.0:* users:("sshd",pid=575,fd=3))
全 14 ページ中 1 ページ目を表示しています。
全 66 問中 1-5 問目を表示しています。
 1397 お客様のコメント最新のコメント 「一部の類似なコメント・古いコメントは隠されています」
CKSの問題集は明確でわかりやすかったです。そしてきのう試験に受かりました。前にもPassTestにLFCSとかCilium-Associateを買って全部合格したもん。ここ合格率高ぇな
Komaki

他社と比べると、たいへんよくなった受験対策問題集です。
他の方のレビューにもありますが、非常によくなっています。
この本でほぼ確実にCKS試験に合格できると思います。
鸟越**

単語とその簡単な説明が多く物足りなさを感じましたが、CKS試験自体がそういうレベルなのでこれでいいのだと思います。
明確に要点を把握できる構成もなかなか良いと感じる。
Kondou
とうたうだけあって、丁寧に解説されています。
効率的にまとまっているCKS参考書だと思います。
Nonami
内容はまあまあ分かりやすいんです。このCKS問題集で殆ど十分だと思われます。
Machida
お陰さまでCKS試験に合格しました!CKS試験参考書が本当に助かりました!誠にありがとうございました。
Sato
本番試験に受験してスムーズに書けて、無事に受かりました。
Kawabe
すごく良いCKSの問題集だと思います。暗記が勝負のところがあるので
Yoshinaga
とりあえずこれさえ取得すれば大丈夫です。一般的に通用します。CKS問題集を使って簡単に試験に受かることができました。ありがとねPassTestさん
Horiguchi
CKS試験受かりました!すべて何も知らない素人の中の素人でしたが、この本を読んで、大体理解できたと思います!
徳永**
Linux Foundationから提供されたCKS問題集のおかげで試験に合格しました。同僚におすすめしようと思います。ありがとうございました。
戸田**
PassTestのこの問題集は読むのもあまり苦がなく勉強のコツが嬉しい内容でPassTestブレイクしつつなるほどな
宫前**
Linux Foundation素晴らしい問題集になっております。CKS試験に受かりましたよ。
田中**
試験合格できました。本番のテストには本当に模擬問題ドンピシャの設問を出ました。試験勉強ならやっぱりこの問題集です!ありがとうございました。
Mita
CKS問題集には丁寧な解説がひたすら書いてあります。次はLFCSに挑戦していきたいと思います。
Andoh
PassTestさんからアプリバージョンを買いまして、隙間時間にも学習が進められます。相性もあると思いますが、自分には合っていました。
Tomita
御社の試験対応問題集は大変役立っています。CKSを勉強して合格することができました。
ありがとうございました。
福田**
無事にCKSの試験に受かりました。このCKS問題集は使いこなせるのであれば私が一番おすすめする問題集
Sakurai
これCKS一冊あれば十分に事足りると私は思いました。わかりやすい!ありがとうございました。
小川**
PassTestさんの押さえるべきポイントを確実に覚えればなかなかCKS試験でいい点は取れると思う。
Kawakami
説明が非常に分かりやすくPassTestの問題集は、短時間内に受験したい人におすすめだな。すべての問題を暗記して言ったら絶対合格すると思うよ。だって試験問題のほとんどがこの問題集に収めたんだもん。
堀ち**
セキュリティ&プライバシー
我々は顧客のプライバシーを尊重する。McAfeeセキュリティサービスを使用して、お客様の個人情報および安心のために最大限のセキュリティを提供します。
365日無料アップデート
購入日から365日無料アップデートをご利用いただけます。365日後、更新版がほしく続けて50%の割引を与えれます。

返金保証
購入後60日以内に、試験に合格しなかった場合は、全額返金します。 そして、無料で他の製品を入手できます。
インスタントダウンロードCKS
お支払い後、弊社のシステムは、1分以内に購入した商品をあなたのメールボックスにお送りします。 2時間以内に届かない場合に、お問い合わせください。
関連製品
関するブログ
- [2026年更新]CKS.PDFの問題回答PDFサンプル問題現実的 [Q66-Q83]
- 2026年最新の100%試験高合格率CKS問題集PDF [Q75-Q99]
- CKS PDF問題集で2026年01月04日最近更新された問題 [Q70-Q86]
- 無料提供中のCKS試験問題集で(2025年最新のPDF問題集)信頼度の高いテストエンジン [Q29-Q51]
- [更新されたのは2025年]Linux Foundation CKS問題準備には無料サンプルのPDF [Q24-Q47]
- [2025年02月27日] 信頼され続けるCKS試験のコツがあるPDF試験材料 [Q25-Q49]
- 問題集は全額返金保証付きのCKS問題集最大50%オフ [Q18-Q34]
- [2024年11月21日] 365日更新、有効なCKS知能問題集 [Q25-Q49]
- リアルなCKS最新試験は2024年最新のCKS練習テスト問題集を提供しています [Q11-Q34]
- CKS PDF問題集で2024年01月14日試験問題 有効なCKS問題集 [Q26-Q43]
