

[2025年04月] 合格させるPCNSC試験一発合格、最新のPCNSC PassTestの提供する試験問題
Paloalto Certifications and Accreditations問題集でPCNSC試験の完全版解答試験学習ガイド
PCNSC認定は、様々な規模の組織におけるネットワークセキュリティインフラの管理を担当するプロフェッショナルに最適です。ネットワークセキュリティの技術とソリューションに関するスキルと知識を向上させたいという個人にも適しています。この認定はベンダー固有であり、Palo Alto Networks製品に焦点を当てているため、これらのソリューションを使用するプロフェッショナルにとって貴重な資格です。
質問 # 34
What type of NAT rule is required to translate an internal server's private IP address to a public IP address for external access?
- A. Source NAT
- B. Bidirectional NAT
- C. Destination NAT
- D. Dynamic NAT
正解:C
質問 # 35
A user's traffic traversing a Palo Alto Networks NGFW sometime can reach http//www company com At the session times out.
The NGFW has been configured with a PBF rule that the user's traffic matches when it goes to http //www company com.
How con the firewall be configured to automatically disable the PBF rule if the next hop goes down?
- A. Create and add a Monitor Profile with an action of Wait Recover in the PBF rule in question.
- B. Configure path monitoring for tine next hop gateway on the default route in tin- virtual router.
- C. Enable and configure a Link Monitoring Profile for the external interface of the firewall.
- D. Create and add a Monitor Profile with an action of Fail Over in the PBF rule in question.
正解:D
質問 # 36
In preparation for a cutover event, what two processes or procedures should be verified? (Choose two)
- A. logging and reporting
- B. auditing
- C. roles and responsibilities
- D. change management requirements
正解:C、D
解説:
For any cutover event, especially when dealing with network security infrastructure like Palo Alto Networks firewalls, it is critical to ensure that:
* Change Management Requirements (B):This involves verifying that all planned changes have been approved, documented, and communicated to all relevant stakeholders. The change management process ensures that any modifications are controlled, predictable, and include a rollback plan in case of issues.
Reference: Palo Alto Networks Best Practices for Change Management Documentation.
* Roles and Responsibilities (C):Clearly defined roles and responsibilities ensure that everyone involved knows their specific tasks during the cutover. This reduces confusion, ensures accountability, and helps in the smooth execution of the cutover plan. It includes defining who is responsible for specific tasks, who needs to be notified, and who has the authority to make decisions. Reference: Palo Alto Networks Operational Best Practices Documentation.
質問 # 37
Identity the Stakeholder with their Role when planning a Firewall Panorama, and Cortex XDR Deployment
正解:
解説:
Explanation:
* Security Engineer- Determines the security, logging, reporting requirements and manages the policy.
* System Administrator- Manages the software distribution method for the Cortex XDR Client.
* Security Operations Analyst- Manages the alerts and responds to threats identified on the network or endpoints.
* Network Engineer- Manages the routing, switching, and general device interconnectivity.
When planning a deployment involving Firewall, Panorama, and Cortex XDR, each stakeholder plays a specific role:
* Security Engineer- This role involves defining and managing security policies, logging configurations, and reporting requirements to ensure compliance and optimal security posture. They are responsible for the overall security configuration and implementation.
質問 # 38
A client has a sensitive application server in their data center and is particularly concerned about resource exhaustion because of distributed denial-of-service attacks.
How can the Palo Alto Networks NGFW be configured to specifically protect tins server against resource exhaustion originating from multiple IP address (DDoS attack)?
- A. Add a DoS Protection Profile with defined session count.
- B. Define a custom App-ID to ensure that only legitimate application traffic reaches the server
- C. Add QoS Profiles to throttle incoming requests.
- D. Add a Vulnerability Protection Profile to block the attack.
正解:A
質問 # 39
Your customer believes that the Panorama appliance is being overwhelmed by the logs from deployed Palo Alto Networks Next-Generation Firewalls.What CLl command can you run to determine the number oflogs per second sent by each firewall?
- A. logging status
- B. show log traffic
- C. debug log-sender statistics
- D. debug log-receiver statistics
正解:D
解説:
To determine the number of logs per second sent by each firewall to a Panorama appliance, the appropriate CLI command to use is:
D:debug log-receiver statistics
This command provides detailed statistics about the logs being received by the Panorama, including the rate at which logs are being sent by each connected firewall. This information can help identify whether the Panorama is being overwhelmed by the volume of logs and which firewalls are contributing the most to the log traffic.
References:
* Palo Alto Networks - CLI Commands for Troubleshooting Panorama: https://docs.paloaltonetworks.com
* Palo Alto Networks - Managing Logs and Log Forwarding:
https://knowledgebase.paloaltonetworks.com
質問 # 40
An administrator needs to optimize traffic to prefer business-critical applications over non-critical applications.
QoS natively integrates with which feature to provide service quality?
- A. port inspection
- B. App-ID
- C. certification revocation
- D. Content-ID
正解:B
質問 # 41
Which of the following Palo Alto Networks features can help reduce the attack surface by limiting the number of applications allowed through the firewall?
- A. App-ID
- B. URL Filtering
- C. Content-ID
- D. User-ID
正解:A
質問 # 42
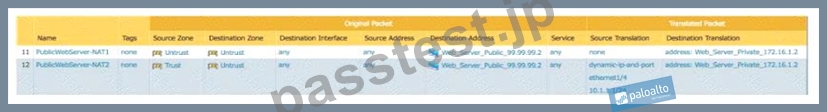
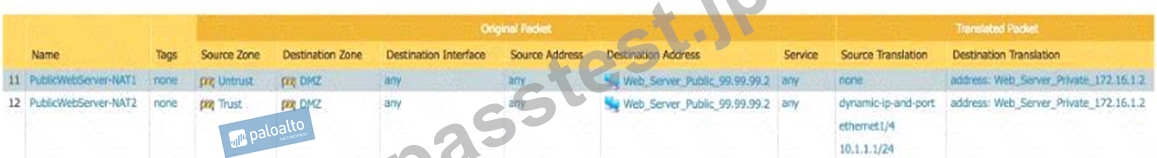
You are hosting a public-facing web server on your DMZ and access to that server is through a Palo Alto Networks firewall Both internal clients and internet clients access this web server using the FQDN public webserver acme com which resolves to the public address of 99.99 99.2 Which combination of NAT policies is necessary to enable access to the web server for both internal and internet clients?
- A.

- B.
- C.
- D.

正解:A
解説:
To enable access to a public-facing web server for both internal and internet clients using the FQDNpublic.webserver.acme.com, which resolves to the public address99.99.99.2, the necessary combination of NAT policies is:C.Option C
* Policy 11: DMZ to Untrust
* Source Zone: DMZ
* Destination Zone: Untrust
* Destination Address:Web_Server_Public_99.99.99.2
* Destination Translation:address: Web_Server_Private_172.16.1.2
* Policy 12: Untrust to Untrust
* Source Zone: Untrust
* Destination Zone: Untrust
* Destination Address:Web_Server_Public_99.99.99.2
* Destination Translation:address: Web_Server_Private_172.16.1.2
These policies ensure that traffic destined for the public IP address99.99.99.2from both the DMZ and Untrust zones is properly translated to the internal web server's private IP address172.16.1.2.
References:
* Palo Alto Networks - NAT Configuration:
https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-admin/networking/nat/nat-policy-rules
質問 # 43
Which two methods can be configured to validate the revocation status of a certificate? (Choose two)
- A. SSL /TLS Service Profile
- B. CRT
- C. CRL
- D. OCSP
- E. Cert-Validation-Profile
正解:B、E
質問 # 44
How can you ensure that a Palo Alto Networks firewall does not block traffic during a software update?
- A. Enable the Suspend Traffic During Upgrade option
- B. Use the High Availability feature
- C. Configure session synchronization
- D. Schedule the upgrade during a maintenance window
正解:D
質問 # 45
Which feature prevents the submission of login information into website froms?
- A. data filtering
- B. credential phishing prevention
- C. file blocking
- D. User-ID
正解:B
質問 # 46
A customer is adding a new site-to-site tunnel from a PaloAlto Networks NGFW to a third party with a policy based VPN peer After the initial configuration is completed and the changes are committed, phase 2 fails to establish Which two changes may be required to fix the issue? (Choose two)
- A. Verify that PFS is enabled on both ends
- B. Add proxy IDs to the iPsec tunnel configuration
- C. Verity that the certificate used tor authentication is installed.
- D. Enable the NAT Traversal advanced option.
正解:A、B
解説:
When configuring a site-to-site VPN between a Palo Alto Networks Next-Generation Firewall (NGFW) and a third-party device with a policy-based VPN peer, Phase 2 failures can often be attributed to configuration mismatches or missing parameters. Here are the two changes that may be required to fix the issue:
B:Verify that PFS is enabled on both ends: Perfect Forward Secrecy (PFS) is a method that ensures the security of cryptographic keys. Both ends of the VPN tunnel need to agree on whether PFS is used. If PFS is enabled on one side but not the other, Phase 2 will fail. Verify the PFS settings and ensure they are matched on both the Palo Alto firewall and the third-party VPN device.
D:Add proxy IDs to the IPsec tunnel configuration: Proxy IDs (or traffic selectors) define the specific local and remote IP ranges that are allowed to communicate through the VPN tunnel.They are particularly crucial when dealing with policy-based VPNs. If the proxy IDs are not correctly configured, Phase 2 negotiations will fail. Add the appropriate proxy IDs to the IPsec tunnel configuration to match the policy-based VPN settings of the third-party device.
References:
* Palo Alto Networks - Configuring Site-to-Site VPN Between Palo Alto Networks and a Third-Party Firewall: https://docs.paloaltonetworks.com
* Palo Alto Networks - VPN Configuration Guidelines: https://knowledgebase.paloaltonetworks.com
質問 # 47
Which feature can be configured on VM-Series firewalls'?
- A. multiple virtual systems
- B. Globallprotect
- C. aggregate interlaces
- D. machine learning
正解:B
質問 # 48
A web server is hosted in the DMZ and the server re configured to listen for income connections on TCP port
443. A Security policies rules allowing access from the Trust zone to the DMZ zone needs to be configured to allow web-browsing access. The web server host its contents over Traffic from Trust to DMZ is being decrypted with a Forward Proxy rule.
Which combination of service and application, and order of Security policy rules needs to be configured to allow cleaned web-browsing traffic to the server on tcp/443?
- A. Rule #1application web-browsing, service service imp action allow
Rule #2 application ssl. service application -default, action allow - B. Rule# 1 application: ssl; service application-default: action allow
Role # 2 application web browsing, service application default, action allow - C. Rule#1 application web-brows.no service application-default, action allow Rule #2 application ssl. Service application-default, action allow
- D. Rule#1application: web-biows.no; service service-https action allow
Rule#2 application ssl. Service application-default, action allow
正解:C
質問 # 49
An administrator sees several inbound sessions identified as unknown tcp in the Traffic logs. The administrator determines that these sessions are from external users accessing the company's propriety accounting application. The administrator wants to reliability identity this as their accounting application and to scan this traffic for threats.
Which option would achieve this result?
- A. Create a custom App-ID and use the "ordered condition cheek box.
- B. Create an Application Override policy and a custom threat signature for the application.
- C. Create an Application Override policy
- D. Create a custom App-ID and enable scanning on the advanced tab.
正解:B
質問 # 50
An organization has Palo Alto Networks MGfWs that send logs to remote monitoring and security management platforms. The network team has report has excessive traffic on the corporate WAN. How could the Palo Alto Networks NOFW administrator reduce WAN traffic while maintaining support for all the existing monitoring/security platforms?
- A. Forward logs from external sources to Panorama for correlation, arid from Panorama send to the NGFW
- B. Any configuration on an M-500 would address the insufficient bandwidth concerns.
- C. Configure log compression and optimization features on all remote firewalls.
- D. forward logs from firewalls only to Panorama, and have Panorama forward log* lo other external service.
正解:D
質問 # 51
Instead of disabling App-IDs regularly, a security policy rule is going to be configured to temporarily allow new App-IDs. In which two circumstances is it valid to disable App-IDs as part of content update-?
(Choose two)
- A. when an organization operates a mission-critical network and has zero tolerance for downtime
- B. when planning to enable the App-IDs immediately
- C. when disabling facebook-base to disable all other Facebook App-IDs
- D. when you want to immediately benefit from the latest threat prevention
正解:A、D
解説:
Disabling App-IDs as part of a content update can be valid in the following circumstances:
B:When you want to immediately benefit from the latest threat prevention: Disabling certain App-IDs can help ensure that the latest threat prevention measures are applied without waiting for the App-IDs to be fully tested in a specific environment. This can be crucial in quickly addressing emerging threats.
D:When an organization operates a mission-critical network and has zero tolerance for downtime: In such environments, administrators might temporarily disable new or modified App-IDs to avoid potential disruptions caused by unverified or untested App-IDs. This ensures that the network remains stable and functional while the new App-IDs are evaluated in a controlled manner.
References:
* Palo Alto Networks - Best Practices for Application and Threat Content Updates:
https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-admin/app-id/manage-app-id/application-and-threat
* Palo Alto Networks - Application and Threat Content Release Notes:
* https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-release-notes/application-and-threat-content-release
質問 # 52
What should an administrator consider when planning to revert Panorama to a pre-PAN-OS 8.1 version?
- A. Administrators need to manually update variable characters to those to used in pre-PAN-OS 8.1.
- B. An administrator must use the Expedition tool to adapt the configuration to the pre-pan-OS 8.1 state.
- C. When Panorama is reverted to an earlier PAN-OS release, variable used in template stacks will be removed authentically.
- D. Panorama cannot be reverted to an earlier PAN-OS release if variables are used in templates or stacks.
正解:D
質問 # 53
What configuration is necessary for Active/Active HA to synchronize sessions between peers?
- A. Enable session preemption on both peers
- B. Enable session synchronization under the HA settings
- C. Configure a floating IP address
- D. Use the same virtual IP address on both peers
正解:B
質問 # 54
What is the default port used by the Terminal Services agent to communicate with a firewall?
- A. 0
- B. 1
- C. 2
- D. 3
正解:B
解説:
The default port used by the Terminal Services agent to communicate with a Palo Alto Networks firewall is5007. The Terminal Services agent (TS agent) integrates with Microsoft Terminal Services to associate user information with sessions, enabling User-ID to accurately map user identities to security policies. Reference:
Palo Alto Networks Terminal Services Agent Documentation.
質問 # 55
Which of the following WildFire action settings will ensure that a malicious file is quarantined and prevented from spreading?
- A. Alert
- B. Block
- C. Allow
- D. Reset-Both
正解:B
質問 # 56
Which two action would be part of an automatic solution that would block sites with untrusted certificates without enabling SSL forward proxy? (Choose two.)
- A. Create a no-decrypt Decryption Policy rule.
- B. Configure an EDL to pull IP Addresses of known sites resolved from a CRL.
- C. Enable the "Block seasons with untrusted Issuers- setting.
- D. Create a Security Policy rule with vulnerability Security Profile attached.
- E. Configure a Dynamic Address Group for untrusted sites.
正解:C、D
質問 # 57
Which GlobalProtect feature ensures that only trusted endpoints can connect to the network?
- A. Host Information Profile (HIP)
- B. App-ID
- C. SSL Decryption
- D. User-ID
正解:A
質問 # 58
......
正真正銘のベスト材料はPCNSCオンライン練習試験:https://www.passtest.jp/Palo-Alto-Networks/PCNSC-shiken.html
最高品質のPCNSC問題集と解釈が待ってます!今すぐ取得せよ:https://drive.google.com/open?id=140fLqx5SxQ4mdGrU1180Ymf_W7L8tWr8