

312-50v12日本語試験問題集、312-50v12日本語練習テスト問題
PDF問題(2025年最新)実際のECCouncil 312-50v12日本語試験問題
質問 # 46
Nedved は、自国の銀行の IT セキュリティ マネージャーです。ある日、電子メール サーバーから不明な IP アドレスへの疑わしい接続を分析した結果、会社の電子メール サーバーにセキュリティ侵害が発生していることが分かりました。
インシデント対応チームに連絡する前に、ネドベドが最初に行う必要があることは何ですか?
- A. 接続をバックアップメールサーバーに移行します
- B. ファイアウォールから疑わしいIPアドレスへの接続をブロックします
- C. そのままにして、すぐにインシデント対応チームに連絡してください
- D. メールサーバーをネットワークから切断する
正解:D
質問 # 47
顧客のリソースが他の顧客のリソースからどの程度分離されているかに応じて、複数のクラウド展開オプションがあります。共有環境ではコストが共有され、各顧客は運用コストを削減できます。1 つのソリューションは、顧客がユーザーまたは組織のグループに参加してクラウド環境を共有することです。このクラウド展開オプションは何と呼ばれますか?
- A. プライベート
- B. パブリック
- C. ハイブリッド
- D. コミュニティ
正解:D
解説:
The purpose of this idea is to permit multiple customers to figure on joint projects and applications that belong to the community, where it's necessary to possess a centralized clouds infrastructure. In other words, Community Cloud may be a distributed infrastructure that solves the precise problems with business sectors by integrating the services provided by differing types of clouds solutions.
The communities involved in these projects, like tenders, business organizations, and research companies, specialise in similar issues in their cloud interactions. Their shared interests may include concepts and policies associated with security and compliance considerations, and therefore the goals of the project also .
Community Cloud computing facilitates its users to spot and analyze their business demands better.
Community Clouds could also be hosted during a data center, owned by one among the tenants, or by a third-party cloud services provider and may be either on-site or off-site.
Community Cloud Examples and Use CasesCloud providers have developed Community Cloud offerings, and a few organizations are already seeing the advantages . the subsequent list shows a number of the most scenarios of the Community Cloud model that's beneficial to the participating organizations.
* Multiple governmental departments that perform transactions with each other can have their processing systems on shared infrastructure. This setup makes it cost-effective to the tenants, and may also reduce their data traffic.
Benefits of Community CloudsCommunity Cloud provides benefits to organizations within the community, individually also as collectively. Organizations don't need to worry about the safety concerns linked with Public Cloud due to the closed user group.
This recent cloud computing model has great potential for businesses seeking cost-effective cloud services to collaborate on joint projects, because it comes with multiple advantages.
Openness and ImpartialityCommunity Clouds are open systems, and that they remove the dependency organizations wear cloud service providers. Organizations are able to do many benefits while avoiding the disadvantages of both public and personal clouds.
* Ensures compatibility among each of its users, allowing them to switch properties consistent with their individual use cases. They also enable companies to interact with their remote employees and support the utilization of various devices, be it a smartphone or a tablet. This makes this sort of cloud solution more flexible to users' demands.
* Consists of a community of users and, as such, is scalable in several aspects like hardware resources, services, and manpower. It takes under consideration demand growth, and you simply need to increase the user-base.
Flexibility and ScalabilityHigh Availability and ReliabilityYour cloud service must be ready to make sure the availability of knowledge and applications in the least times. Community Clouds secure your data within the same way as the other cloud service, by replicating data and applications in multiple secure locations to guard them from unforeseen circumstances.
Cloud possesses redundant infrastructure to form sure data is out there whenever and wherever you would like it. High availability and reliability are critical concerns for any sort of cloud solution.
Security and ComplianceTwo significant concerns discussed when organizations believe cloud computing are data security and compliance with relevant regulatory authorities. Compromising each other's data security isn't profitable to anyone during a Community Cloud.
* the power to dam users from editing and downloading specific datasets.
* Making sensitive data subject to strict regulations on who has access to Sharing sensitive data unique to a specific organization would bring harm to all or any the members involved.
* What devices can store sensitive data.
Users can configure various levels of security for his or her data. Common use cases:Convenience and ControlConflicts associated with convenience and control don't arise during a Community Cloud. Democracy may be a crucial factor the Community Cloud offers as all tenants share and own the infrastructure and make decisions collaboratively. This setup allows organizations to possess their data closer to them while avoiding the complexities of a personal Cloud.
Less Work for the IT DepartmentHaving data, applications, and systems within the cloud means you are doing not need to manage them entirely. This convenience eliminates the necessity for tenants to use extra human resources to manage the system. Even during a self-managed solution, the work is split among the participating organizations.
Environment SustainabilityIn the Community Cloud, organizations use one platform for all their needs, which dissuades them from investing in separate cloud facilities. This shift introduces a symbiotic relationship between broadening and shrinking the utilization of cloud among clients. With the reduction of organizations using different clouds, resources are used more efficiently, thus resulting in a smaller carbon footprint.
質問 # 48
マルチホーム ファイアウォールのネットワーク接続の最小数はいくつですか?
- A. 0
- B. 1
- C. 2
- D. 3
正解:C
質問 # 49
バッファオーバーフローエクスプロイトをプログラミングしていて、プログラムexploit.cに200バイトのNOPスレッドを作成したいとします。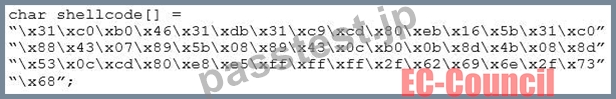
NOP 命令の 16 進数値は何ですか?
- A. 0x60
- B. 0x90
- C. 0x70
- D. 0x80
正解:B
質問 # 50
あなたはサイバーセキュリティの熱心な新進気鋭として、ワイヤレス ネットワーク セキュリティについてさらに学ぶために自宅に小さなラボを設置しました。自宅の Wi-Fi ネットワークで実験しているときに、よく知られたハッキング ツールを使用してネットワーク トラフィックをキャプチャし、Wi-Fi パスワードを解読しようと試みることにしました。しかし、何度も試みましたが、成功しませんでした。自宅の Wi-Fi ネットワークでは、AES 暗号化による WPA2 Personal が使用されています。
Wi-Fi パスワードを解読するのが難しいのはなぜですか?
- A. ネットワークは解読不可能な暗号化方式を使用しています
- B. ネットワークは MAC アドレス フィルタリングを使用しています。
- C. Wi-Fi パスワードが複雑で長すぎます
- D. あなたのハッキングツールは時代遅れです
正解:A
解説:
The network is using an uncrackable encryption method, which makes it difficult to crack the Wi-Fi password.
WPA2 Personal with AES encryption is the strongest form of security offered by Wi-Fi devices at the moment, and it should be used for all purposes. AES stands for Advanced Encryption Standard, and it is a symmetric-key algorithm that uses a 128-bit, 192-bit, or 256-bit key to encrypt and decrypt data. AES is considered to be uncrackable by brute force attacks, as it would take an impractical amount of time and computational power to try all possible key combinations12. Therefore, unless you have access to the Wi-Fi password or the encryption key, you will not be able to decrypt the network traffic and crack the password.
The other options are not correct for the following reasons:
* A. The Wi-Fi password is too complex and long: This option is not relevant because the Wi-Fi password is not directly used to encrypt the network traffic. Instead, the password is used to generate a Pre-Shared Key (PSK), which is then used to derive a Pairwise Master Key (PMK), which is then used to derive a Pairwise Transient Key (PTK), which is then used to encrypt the data. Therefore, the complexity and length of the password do not affect the encryption strength, as long as the password is not easily guessed or leaked34.
* B. Your hacking tool is outdated: This option is not plausible because even if your hacking tool is outdated, it would not affect your ability to capture the network traffic and attempt to crack the password. The hacking tool may not support the latest Wi-Fi standards or protocols, but it should still be able to capture the raw data packets and save them in a file. The cracking process would depend on the encryption algorithm and the key, not on the hacking tool.
* D. The network is using MAC address filtering: This option is not feasible because MAC address filtering is a technique that restricts network access and communication to trusted devices based on their MAC addresses, which are unique identifiers assigned to network interfaces. MAC address filtering can prevent unauthorized devices from joining the network, but it cannot prevent authorized devices from capturing the network traffic. Moreover, MAC address filtering can be easily bypassed by spoofing the MAC address of an allowed device56.
References:
* 1: What is AES Encryption and How Does it Work? | Kaspersky
* 2: AES Encryption: Everything You Need to Know | Comparitech
* 3: How Does WPA2 Work? | Techwalla
* 4: How Does WPA2 Encryption Work? | Security Boulevard
* 5: What is MAC Address Filtering? | Definition, Types & Examples - Fortinet
* 6: How to Bypass MAC Address Filtering on Wireless Networks - Null Byte :: WonderHowTo
質問 # 51
コンピュータの 1 つにルートキットがインストールされていることが判明した場合、最善の代替策は何でしょうか?
- A. ファイルを削除してソースを特定します
- B. 正常に動作することが確認されているシステムからシステムファイルをコピーします
- C. トラップとトレースを実行する
- D. 正常なメディアから再ロードする
- E. 以前のバックアップから再ロード
正解:D
質問 # 52
次のコマンドは何に使用されますか?
ネット使用\targetipc$ "" /u:""
- A. SAM の取得
- B. このコマンドはヌルセッションとして接続するために使用されます
- C. Cisco ルータの列挙
- D. etc/passwd ファイルを取得する
- E. Samba 経由で Linux コンピュータに接続します。
正解:B
質問 # 53
ポートが開いている場合の NULL スキャンに対する適切な応答は何ですか?
- A. RST
- B. FIN
- C. ACK
- D. PSH
- E. SYN
- F. 応答なし
正解:F
質問 # 54
デジタル署名に関して正しいのは何ですか?
- A. デジタル署名は、署名者の秘密鍵で暗号化された元の文書のハッシュであるため、署名された文書間で移動することはできません。
- B. デジタル署名は、同じ種類の異なるドキュメントで使用できます。
- C. デジタル署名はユーザーごとに 1 回発行され、有効期限が切れるまでどこでも使用できます。
- D. デジタル署名はドキュメント コンテンツの単純なハッシュであるため、署名されたドキュメント間で移動することはできません。
正解:A
質問 # 55
SQL インジェクション (SQLi) 攻撃は、Web リクエストに SQL 構文を挿入しようとします。これにより、認証がバイパスされ、攻撃者が Web アプリケーションに添付されたデータにアクセスしたり、データを変更したりできるようになります。
次の SQLI タイプのうち、データベース サーバーの DNS 要求機能を利用してデータを攻撃者に渡すものはどれですか。
- A. ユニオンベースのSQLI
- B. 時間ベースのブラインドSQLI
- C. 帯域外SQLI
- D. インバンドSQLI
正解:C
解説:
Out-of-band SQL injection occurs when an attacker is unable to use an equivalent channel to launch the attack and gather results. ... Out-of-band SQLi techniques would believe the database server's ability to form DNS or HTTP requests to deliver data to an attacker. Out-of-band SQL injection is not very common, mostly because it depends on features being enabled on the database server being used by the web application.
Out-of-band SQL injection occurs when an attacker is unable to use the same channel to launch the attack and gather results.
Out-of-band techniques, offer an attacker an alternative to inferential time-based techniques, especially if the server responses are not very stable (making an inferential time-based attack unreliable).
Out-of-band SQLi techniques would rely on the database server's ability to make DNS or HTTP requests to deliver data to an attacker. Such is the case with Microsoft SQL Server's xp_dirtree command, which can be used to make DNS requests to a server an attacker controls; as well as Oracle Database's UTL_HTTP package, which can be used to send HTTP requests from SQL and PL/SQL to a server an attacker controls.
質問 # 56
ジョーはある組織の IT 管理者として働いており、最近その組織のためにクラウド コンピューティング サービスを立ち上げました。このサービスを実装するために、彼は通信会社に連絡を取り、組織とクラウド サービス プロバイダー間のインターネット接続とトランスポート サービスを提供してもらいました。NIST クラウド展開リファレンス アーキテクチャでは、上記のシナリオにおいて通信会社はどのカテゴリに分類されますか。
- A. クラウド消費者
- B. クラウドブッカー
- C. 雲のキャリア
- D. クラウド監査人
正解:C
解説:
A cloud carrier acts as an intermediary that provides connectivity and transport of cloud services between cloud consumers and cloud providers.
Cloud carriers provide access to consumers through network, telecommunication and other access devices. for instance, cloud consumers will obtain cloud services through network access devices, like computers, laptops, mobile phones, mobile web devices (MIDs), etc.
The distribution of cloud services is often provided by network and telecommunication carriers or a transport agent, wherever a transport agent refers to a business organization that provides physical transport of storage media like high-capacity hard drives.
Note that a cloud provider can started SLAs with a cloud carrier to provide services consistent with the level of SLAs offered to cloud consumers, and will require the cloud carrier to provide dedicated and secure connections between cloud consumers and cloud providers.
質問 # 57
インシデント調査員は、セキュリティ侵害の可能性がある組織のネットワーク上のすべてのファイアウォール、プロキシ サーバー、および侵入検知システム (IDS) からイベント ログのコピーを受け取るように依頼します。調査員がすべてのログの情報を相関させようとすると、ログに記録されたイベントの多くの順序が一致しません。
最も可能性の高い原因は何でしょうか?
- A. ネットワークデバイスがすべて同期されていません。
- B. ログの収集中に適切な保管チェーンが遵守されませんでした。
- C. 攻撃者がログからイベントを変更または消去しました。
- D. セキュリティ侵害は誤検知でした。
正解:A
解説:
Many network and system administrators don't pay enough attention to system clock accuracy and time synchronization. Computer clocks can run faster or slower over time, batteries and power sources die, or daylight-saving time changes are forgotten. Sure, there are many more pressing security issues to deal with, but not ensuring that the time on network devices is synchronized can cause problems. And these problems often only come to light after a security incident.
If you suspect a hacker is accessing your network, for example, you will want to analyze your log files to look for any suspicious activity. If your network's security devices do not have synchronized times, the timestamps' inaccuracy makes it impossible to correlate log files from different sources. Not only will you have difficulty in tracking events, but you will also find it difficult to use such evidence in court; you won't be able to illustrate a smooth progression of events as they occurred throughout your network.
質問 # 58
侵入テスト担当者は、ライブ ホストを見つけるために大規模なネットワーク範囲をスキャンするように指示されました。ネットワークは、ファイアウォールで厳格な TCP フィルタリング ルールを使用していることで知られており、これが一般的なホスト検出手法の妨げとなる可能性があります。テスト担当者は、これらのファイアウォールの制限を回避し、ライブ システムを正確に識別できる方法を必要としています。テスト担当者は、どのホスト検出手法を使用すべきでしょうか。
- A. lCMP ECHO Pingスキャン
- B. UDP Pingスキャン
- C. ICMP タイムスタンプ Ping スキャン
- D. TCP SYN Pingスキャン
正解:D
解説:
The host discovery technique that the tester should use is TCP SYN Ping Scan. This technique sends a TCP SYN packet to a specified port on the target host and waits for a response. If the host responds with a TCP SYN/ACK packet, it means the host is alive and the port is open. If the host responds with a TCP RST packet, it means the host is alive but the port is closed. If the host does not respond at all, it means the host is either dead or filtered by a firewall12. TCP SYN Ping Scan can bypass firewall restrictions because it mimics the initial stage of a TCP three-way handshake, which is a common and legitimate network activity. Therefore, most firewalls will allow TCP SYN packets to pass through and reach the target host, unless they are configured to block specific ports or IP addresses3. TCP SYN Ping Scan can also accurately identify live systems because it does not rely on ICMP, which may be blocked or rate-limited by some firewalls or routers.
The other options are not as effective or feasible as TCP SYN Ping Scan for the following reasons:
* A. UDP Ping Scan: This technique sends a UDP packet to a specified port on the target host and waits for a response. If the host responds with an ICMP Port Unreachable message, it means the host is alive but the port is closed. If the host does not respond at all, it means the host is either dead, the port is open, or the packet is filtered by a firewall12. UDP Ping Scan may not bypass firewall restrictions because some firewalls may block or drop UDP packets, especially if they are sent to uncommon or reserved ports. UDP Ping Scan may also not accurately identify live systems because it cannot distinguish between open ports and filtered packets, and it may generate false positives or negatives due to packet loss or rate-limiting.
* B. ICMP ECHO Ping Scan: This technique sends an ICMP ECHO Request packet to the target host and waits for an ICMP ECHO Reply packet. If the host responds with an ICMP ECHO Reply packet, it means the host is alive. If the host does not respond at all, it means the host is either dead or filtered by a firewall12. ICMP ECHO Ping Scan may not bypass firewall restrictions because some firewalls may block or drop ICMP packets, especially if they are sent to prevent ping sweeps or denial-of-service attacks. ICMP ECHO Ping Scan may also not accurately identify live systems because it may generate false positives or negatives due to packet loss or rate-limiting.
* C. ICMP Timestamp Ping Scan: This technique sends an ICMP Timestamp Request packet to the target host and waits for an ICMP Timestamp Reply packet. If the host responds with an ICMP Timestamp Reply packet, it means the host is alive. If the host does not respond at all, it means the host is either dead or filtered by a firewall12. ICMP Timestamp Ping Scan may not bypass firewall restrictions because some firewalls may block or drop ICMP packets, especially if they are sent to prevent ping sweeps or denial-of-service attacks. ICMP Timestamp Ping Scan may also not accurately identify live systems because it may generate false positives or negatives due to packet loss or rate-limiting.
References:
* 1: Host Discovery in Nmap Network Scanning - GeeksforGeeks
* 2: nmap Host Discovery Techniques
* 3: TCP SYN Ping Scan - Nmap
* : Ping Sweep - an overview | ScienceDirect Topics
* : UDP Ping Scan - Nmap
* : UDP Ping Scan - an overview | ScienceDirect Topics
* : ICMP Ping Scan - Nmap
* : ICMP Ping Scan - an overview | ScienceDirect Topics
質問 # 59
以下は、ネットワーク IDS によってキャプチャされたエントリです。このエントリを分析するタスクがあなたに割り当てられます。値 0x90 に気付きました。これは、Intel プロセッサで最も一般的な NOOP 命令です。攻撃者がバッファ オーバーフロー攻撃を試みていることがわかります。
出力の ASCII 部分に「/bin/sh」があることにも気付くでしょう。
アナリストとして、この攻撃についてどのような結論を下しますか?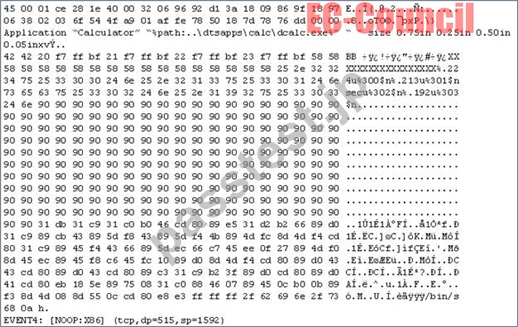
- A. 攻撃者は侵入先のマシンにディレクトリを作成しています
- B. 攻撃者はコマンドラインシェルを起動するエクスプロイトを試みています
- C. バッファオーバーフロー攻撃はIDSによって無効化されました
- D. 攻撃者はバッファオーバーフロー攻撃を試み、成功しました
正解:B
質問 # 60
ある組織の不満を抱いた元従業員のジョンは、組織を悪用するためにプロのハッカーに連絡しました。攻撃の過程で、プロのハッカーは、vktim の 1 つに属するマシンにスキャナーをインストールし、同じネットワーク上の複数のマシンをスキャンして脆弱性を特定し、さらに悪用しました。上記のシナリオでジョンが使用した脆弱性評価ツールの種類は何ですか。
- A. プロキシ スキャナー
- B. エージェントベースのスキャナー
- C. ネットワークベースのスキャナ
- D. クラスタースキャナー
正解:B
解説:
Agent-based scanners reside on a single machine but can scan several machines on the same network.
Network-based scanner
A network-based vulnerability scanner, in simplistic terms, is the process of identifying loopholes on a computer's network or IT assets, which hackers and threat actors can exploit. By implementing this process, one can successfully identify their organization's current risk(s). This is not where the buck stops; one can also verify the effectiveness of your system's security measures while improving internal and external defenses.
Through this review, an organization is well equipped to take an extensive inventory of all systems, including operating systems, installed software, security patches, hardware, firewalls, anti-virus software, and much more.
Agent-based scanner
Agent-based scanners make use of software scanners on each and every device; the results of the scans are reported back to the central server. Such scanners are well equipped to find and report out on a range of vulnerabilities.
NOTE: This option is not suitable for us, since for it to work, you need to install a special agent on each computer before you start collecting data from them.
質問 # 61
次のツールのうち、列挙に使用されるものはどれですか? (3 つ選択してください。)
- A. SID2ユーザー
- B. クフ王
- C. ソーラーウィンズ
- D. ダンプセック
- E. ユーザー2SID
正解:A、D、E
質問 # 62
誤って構成され、詳細なエラー メッセージなどのハッカーにとって有用な情報を提供する可能性のある、Web サーバー上の一般的なファイルは何ですか?
- A. administration.config
- B. idq.dll
- C. httpd.conf
- D. php.ini
正解:D
解説:
The php.ini file may be a special file for PHP. it's where you declare changes to your PHP settings. The server is already configured with standard settings for PHP, which your site will use by default. Unless you would like to vary one or more settings, there's no got to create or modify a php.ini file. If you'd wish to make any changes to settings, please do so through the MultiPHP INI Editor.
質問 # 63
Mirai マルウェアは IoT デバイスをターゲットにしています。侵入後、それらを使用して増殖し、ボットネットを作成し、どのような種類の攻撃を開始するのでしょうか?
- A. MITM攻撃
- B. 誕生日攻撃
- C. パスワード攻撃
- D. DDoS攻撃
正解:D
質問 # 64
......
更新された2025年04月合格させる312-50v12日本語試験リアル練習テスト問題:https://www.passtest.jp/ECCouncil/312-50v12-JPN-shiken.html