

NCP-CI-AWS更新された試験問題集で[2026年最新] 練習有効な試験問題集
NCP-CI-AWSサンプルには正確で更新された問題
Nutanix NCP-CI-AWS 認定試験の出題範囲:
| トピック | 出題範囲 |
|---|---|
| トピック 1 |
|
| トピック 2 |
|
| トピック 3 |
|
| トピック 4 |
|
質問 # 51
Refer to Exhibit: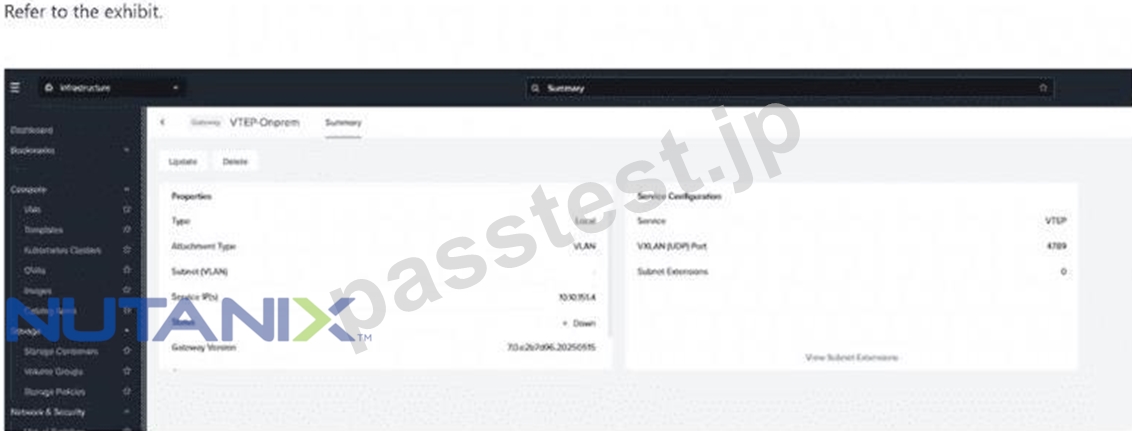
An NC2 cluster on AWS has been deployed with Flow Virtual Networking. The VTEP Gateway on the cluster has been showing as " Down, " preventing a subnet extension from being created. What could be causing this?
- A. The AWS Proxy Server is misconfigured
- B. Multi-cloud Snapshot Technology is claiming ports 4789
- C. The on-premises VTEP gateway is not reachable
- D. Missing routes for PC, NTP and DNS servers
正解:D
解説:
AVTEP (VXLAN Tunnel Endpoint) Gatewayshowing a status of " Down " indicates a connectivity or configuration failure within the control plane. In an NC2 environment, the gateway relies on consistent communication withPrism Central (PC)for management and synchronization, as well asNTP and DNSfor time-sync and name resolution. If the route tables in the AWS VPC are missing the necessary entries to reach these management services, the VTEP gateway will fail to initialize or maintain its heartbeat, resulting in a " Down " status. While on-premises reachability is important for traffic flow, the failure to create the extension entirely usually points to these missing internal routes that prevent the Nutanix software components from coordinating correctly within the cloud environment.
質問 # 52
Where can the status of a Layer 2 Extension be checked within the management interface?
- A. Prism Central > Network and Security > Subnets > Subnet Extensions
- B. Prism Central > Network and Security > Connectivity > Subnet Extensions
- C. Prism Central > Network and Security > Network Services > Subnet Extensions
- D. Prism Central > Network and Security > Virtual Private Clouds > Subnet Extensions
正解:C
質問 # 53
A company wants to start using Nutanix Cloud Clusters (NC2) in AWS. The company has large spend commitments as part of an AWS Enterprise Discount Program (EDP) totaling $15 million.
What approach should the administrator take to ensure that Nutanix licensing costs to the EDP commitment?
- A. Purchase Nutaniz licenses through the AWS Marketplace.
- B. Request a trial license directly from Nutanix
- C. Leverage existing Nutanix licenses.
- D. Purchase Nutanix licenses directly from Nutanix and contact AWS support.
正解:A
解説:
* Given the company ' s large spend commitments as part of an AWS Enterprise Discount Program (EDP) totaling $15 million, purchasing Nutanix licenses through the AWS Marketplace ensures that the costs contribute to the EDP commitment.
* This approach integrates the Nutanix license costs into the overall AWS spend, thereby maximizing the benefits of the EDP.
* Purchasing directly from Nutanix or leveraging existing licenses might not count towards the AWS EDP commitment, and trial licenses are typically for evaluation purposes and do not contribute to the committed spend.
Refer to the Nutanix and AWS documentation on licensing and marketplace purchases, and EDP program details.
質問 # 54
An administrator is planning to leverage NC2 on AWS for an elastic DR scenario where the initial cluster is using 13en.metal.
Which two additional node types are supported for cluster expansion? (Choose two.)
- A. m5d.metal
- B. I3.metal
- C. Z1d.metal
- D. i4i.metal
正解:B、D
解説:
When planning to leverage NC2 on AWS for an elastic DR scenario where the initial cluster is using 13en.
metal, the following additional node types are supported for cluster expansion:
* I3.metal: These instances provide high IOPS and low latency with NVMe SSDs, making them suitable for storage-intensive applications.
* i4i.metal: These instances offer higher performance with AWS Nitro SSDs, improved network bandwidth, and better compute performance compared to the I3.metal instances.
Nutanix Cloud Clusters on AWS Documentation
Amazon EC2 I4i Instances - AWS
Amazon EC2 I3 Instances - AWS
質問 # 55
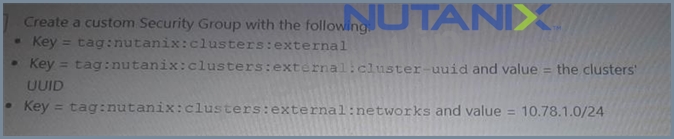
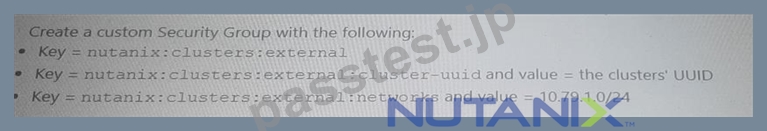
An administrator has deployed an NC2 on AWS cluster that is running mixed workloads. Multiple SQL database are running on the NC2 cluster using a native subnet of 10.78.1.0/24.
The administrator wants to ensure only application servers from source subnet 10.79.1.0/24 that reside outside of the NC2 cluster can access the databases.
Which two actions will help the administrator most securely achieve this? (Choose two.)
- A.
- B.

- C.
- D.

正解:A、C
解説:
To ensure that only application servers from the source subnet 10.79.1.0/24 can access the SQL databases running on the NC2 cluster in the subnet 10.78.1.0/24, the administrator can take the following actions:
* Option A: Create a custom Security Group with the following rules:
* Key = tag:nutanix:clusters
* Key = tag:nutanix:clusters:external and value = the clusters ' UUID
* Key = tag:nutanix:clusters:external and value = 10.78.1.0/24
* Option D: Create a custom Security Group with the following:
* Key = nutanix:clusters
* Key = nutanix:clusters:external and value = the clusters ' UUID
* Key = nutanix:clusters:external and value = 10.79.1.0/24
These actions help create security rules that restrict access to the databases only from the specified source subnet, ensuring secure and controlled access.
Nutanix Cloud Clusters on AWS Administration
AWS Security Groups Documentation
質問 # 56
When configuring an alert email in Prism Central deployed within an NC2 environment, what is required in order for the emails to be sent properly?
- A. SMTP server configured in Prism Central settings
- B. Cluster Super Admin permissions
- C. A whitelisted public cloud console endpoint
- D. Name servers configured in Prism Central
正解:A
解説:
To ensure that alert emails are sent properly from Prism Central within an NC2 environment, configuring an SMTP server in the Prism Central settings is required. The SMTP server facilitates the sending of email notifications for alerts and other communications.
* SMTP Configuration:
* Prism Central requires an SMTP server to send email alerts. This involves specifying the SMTP server address, port, and authentication details if needed.
* The configuration must include the email address from which the alerts will be sent and the recipient addresses.
* Steps to Configure SMTP Server in Prism Central:
* Log in to Prism Central.
* Navigate to the " Settings " menu.
* Select " Email Server " under the " Alerts " section.
* Enter the SMTP server details, including the server address, port, and authentication credentials.
* Test the configuration to ensure emails are sent correctly.
Nutanix Prism Central Administration Guide
Nutanix Support Documentation on Email Alert Configuration
Best Practices for Configuring SMTP Servers in Cloud Environments
質問 # 57
Which two options are prerequisites for deploying an NC2 on AWS cluster? (Choose two.)
- A. An on-premises Prism Central environment
- B. AWS Direct Connect
- C. A valid CIDR range
- D. A my.nutanix.com account
正解:C、D
解説:
A valid CIDR range: A CIDR (Classless Inter-Domain Routing) range is necessary for creating the subnets within the VPC. This range defines the IP address space for the cluster and its components.
A my.nutanix.com account: This account is required to access Nutanix services, including the NC2 console, manage licenses, and perform other administrative tasks.
AWS Direct Connect and an on-premises Prism Central environment are not prerequisites for deploying an NC2 on AWS cluster. While Direct Connect can be used for enhanced network performance and connectivity, it is not a requirement for deployment. Similarly, having an on-premises Prism Central environment is not mandatory for NC2 deployment on AWS.
Reference:
Refer to the Nutanix documentation on NC2 prerequisites and setup guides, and AWS documentation on VPC and subnet creation.
質問 # 58
An administrator has recently deployed an NC2 cluster and has observed that it uses a CloudFormation stack to create IAM roles within AWS. Which statement is correct regarding this NC2 cluster environment?
- A. Information about the CloudFormation stack can be viewed, namely Nutanix-Clusters-High-Nc2-Cloud- Stack-Prod, on the Stacks page of the CloudFormation console.
- B. After running the CloudFormation template, the administrator will never need to run it again.
- C. If an AWS account has already been added to an organization and the administrator wants to add the same AWS account to another organization, the CloudFormation template will need to be created again.
- D. When running the CloudFormation script, the administrator must log into the AWS account with a user role that has the IAMFullAccess and AWSCloudFormationFullAccess permissions.
正解:D
解説:
Deploying NC2 on AWS requires the creation of specific IAM roles and policies to allow the Nutanix service to manage AWS resources like EC2 instances and VPCs. This is typically handled by an automatedCloudFormation stack. For this process to succeed, the AWS user executing the script must possess high-level administrative permissions. Specifically, they requireIAMFullAccessto create the necessary roles andAWSCloudFormationFullAccessto deploy and manage the stack itself. Without these permissions, the CloudFormation template will fail to create the security identities required for the NC2 console to communicate with the AWS API. This is a one-time prerequisite for onboarding the AWS account into the NC2 organization.
質問 # 59
An administrator needs to prepare the steps to recover a cluster using Cluster Protect, where Prism Central is hosted on another cluster. What steps should the administrator take?
- A. Redeploy the cluster using the NC2 consoleMark the broken Cluster to be replaced in the NC2 consoleRedeploy Multi Cloud Snapshot TechnologyRecover the User VMs
- B. Set the Cluster to Failed in the NC2 ConsoleRedeploy Multi Cloud Snapshot TechnologyRedeploy the cluster using the NC2 consoleRecover the User VMs
- C. Set the Cluster to Failed in the NC2 ConsoleRedeploy the cluster using the NC2 consoleRedeploy Multi Cloud Snapshot TechnologyRecover the User VMs
- D. Redeploy the cluster using the NC2 consoleRedeploy Multi Cloud Snapshot TechnologyMark the broken Cluster to be replaced in the NC2 consoleRecover the User VMs
正解:C
解説:
When using the Nutanix Cluster Protect feature to recover a failed NC2 cluster on AWS, and the management Prism Central (PC) instance is hosted on a separate, healthy cluster, a specific orchestration sequence must be followed. The process begins in the NC2 console, where the administrator must manually change the status of the cluster to Failed. This step is critical as it signals the portal to initiate the recovery workflow and release associated cloud resources. Next, the administrator uses the console to redeploy the cluster, which provisions new bare-metal instances and installs the AOS software. Once the infrastructure is ready, Multicloud Snapshot Technology (MST) must be redeployed or re-enabled on the new cluster to re-establish the connection to the Amazon S3 bucket containing the snapshots. Finally, the User VMs (UVMs) are recovered and hydrated from these snapshots. This specific order ensures that the target environment and management links are fully operational before data restoration commences.
質問 # 60
When selecting the NC2 subscription plan from the Nutanix Billing portal, which options are available.
- A. Reserved Instances, Cloud Provider Credits, Bring your own License (BYOL)
- B. Pay-as-you-Go (PayG), Cloud Provider Credits, Bring your own License (BYOL)
- C. Pay-as-you-Go (PayG), Bring your own License (BYOL)
- D. Reserved Instances, Bring your own License (BYOL)
正解:C
解説:
When selecting the NC2 subscription plan from the Nutanix Billing portal, the available options include:
Pay-as-you-Go (PayG): A flexible payment option where users are billed based on their actual usage, providing cost efficiency for variable workloads.
Bring your own License (BYOL): Allows users to utilize existing Nutanix licenses they have purchased, offering a cost-effective way to leverage existing investments in Nutanix software.
Reference:
Refer to the Nutanix billing and subscription documentation for detailed descriptions of subscription plans and their benefits.
質問 # 61
In which two ways should an NC2 on AWS cluster be hibernated manually? (Choose two.)
- A. Select the cluster under NC2 console and Select Hibernate/Resume on the cluster sur page.
- B. Log into Prism Element navigate to Settings and select Hibernate/Resume.
- C. Log into Prism, Central, navigate to Planning, find hibernate and resume.
- D. Log into NC2 console, find the cluster name and select Hibernate/Resume from the ellipses.
正解:A、D
質問 # 62
When AWS reports a System Reboot event for a bare-metal instance, how does the NC2 console respond?
- A. Nutanix restarts the AHV host.
- B. No action is taken.
- C. Nutanix replaces the instance.
- D. Nutanix suspends all VMs on the host.
正解:C
解説:
Nutanix Cloud Clusters (NC2) on AWS is designed to provide a " cloud-native " resilience experience, meaning it proactively manages the underlying hardware health.
If AWS issues a notification for aSystem Rebootor a hardware-related event on a bare-metal instance, the NC2 console does not simply wait for the reboot to occur. To maintain cluster availability and avoid potential data integrity issues during an uncontrolled hardware event, NC2 triggers anautomated host replacement. The system will provision a new bare-metal instance, integrate it into the cluster, and migrate the data and workloads (using High Availability if necessary) away from the degraded or scheduled-to-reboot host. This automation ensures that the Nutanix cluster remains healthy and functional despite the ephemeral nature of cloud infrastructure hardware.
質問 # 63
An NC2 cluster on AWS has been deployed to act as a DR site for an on-premises cluster. A Layer 2 Stretch has been established and the Gateway on-premises is used for all traffic for the subnet from both clusters.
What would be the course of action to restore service should the on-premises Data Center go completely offline?
- A. Failover the VMs and update the Forward policy on the on-premises cluster.
- B. Failover the VMs and remove the Forward policy on the NC2 on AWS cluster.
- C. Failover the VMs and update the Forward policy on the NC2 on AWS cluster.
- D. Failover the VMs and remove the Forward policy on the on-premises cluster.
正解:D
解説:
In a Layer 2 stretched environment where the default gateway resides on-premises, a " Forward policy " is used to route traffic from the cloud back to the data center. If the on-premises data center goes completely offline, the on-premises gateway is no longer reachable, which would halt all North-South communication for the VMs failed over to AWS. To restore full service, the administrator must not only failover the VMs to the NC2 cluster but also remove the Forward policy on the on-premises cluster (or specifically update the routing logic to ensure the AWS cluster takes over gateway duties). This allows the cloud cluster to stop attempting to tunnel traffic to the missing on-premises gateway and instead utilize local cloud-based exit points for network traffic, restoring external connectivity.
質問 # 64
An administrator has deployed an NC2 cluster on AWS to an existing environment for VDI.
Afterwards, the corporate security teams direct the administrator to reuse an existing AWS subnet, 10.79.4.0
/24 that has two EC2 instances: EC2-1 (10.79.4.200) and EC2-2 (10.79.4.201). The security team indicates that this directive is to avoid overlap with the AHV IPAM.
Which two configuration actions should the administrator take to ensure there are no configuration issues?
(Choose two.)
- A. aCLI > net.de/ete_from_ip_blacklist 10.79.4.200 aCLI > net.defete_fromjp_blacklist 10.79.4.201
- B. aCLI > net.add_to_ip_bfacklist 10.79.4.200 aCLI > net.add_to_ip_blacklist 10.79.4.201
- C. Configure the AHV JPAM to use DHCP range 10.79.4.2 -10.79.4.253.
- D. Deploy two VMs on the NC2 cluster and assign 10.79.4.200 and 10.79.4.201 as the assigned IPs in Prism Element
正解:B、C
解説:
To avoid IP address conflicts and ensure there are no configuration issues when reusing an existing AWS subnet, the administrator should take the following actions:
* aCLI > net.add_to_ip_blacklist 10.79.4.200 aCLI > net.add_to_ip_blacklist 10.79.4.201 (Answer A):
* This command adds the specified IP addresses to the blacklist, preventing AHV IPAM from assigning these addresses to any VMs. This ensures that the existing EC2 instances with IPs
10.79.4.200 and 10.79.4.201 are not allocated to other VMs in the NC2 cluster.
* Configure the AHV IPAM to use DHCP range 10.79.4.2 -10.79.4.253 (Answer D):
* By configuring the AHV IPAM to use a specific DHCP range, you ensure that the IP addresses assigned to the EC2 instances (10.79.4.200 and 10.79.4.201) are not included in the DHCP pool.
This prevents IP address conflicts within the subnet.
Nutanix aCLI Reference
Nutanix NC2 on AWS Documentation
AWS VPC and Subnet Basics
質問 # 65
An administrator plans to reserve Nutanix licenses for NC2 consumption.
Which two statements are correct? (Choose two.)
- A. A reserved license can be unreserved and used it for an on-premises cluster by updating the reserved capacity of that license to zero.
- B. Capacity reserved from a license can cover usage for all NC2 clusters associated with that workspace.
- C. The license reservation must be deleted when terminating or hibernating an NC2 cluster.
- D. If one NC2 cluster is terminated and another NC2 cluster is created, the reserved capacity must be manually used to cover the new cluster's usage.
正解:A、B
質問 # 66
An administrator has deployed an NC2 cluster in AWS.
The following configuration decisions were made:
Created a new VPC from the NC2 console as part of the deployment
Selected the Public option for prism access policy
Host type selected was i13en,metal
The administrator now has a goal of provision public internet access to a user VM (UVM),web-1, on the Nutanix cluster. The admin can access Prism Element via the public DNS of the Auto-created load balancer.
The administrator tries to create another network load balancer for the web server access. After creating the load balancer and registering web-1's IP address as a target, the administrator finds that the health check for the VM target is failing and the DNS returns as NOT Found message in the browser.
Why is the issue happening?
- A. The administrator needs to provision an application load balancer instead of a network load balancer to allow Internet traffic to access the UVM subnet.
- B. The administrator has not assigned a public IP to web-1.
- C. The administrator has not modified the inbound rules under the UVM security group to a/low the network load balancer to access the UVM subnet.
- D. The load balancer is still in a Provisioning state.
正解:B
解説:
* For a VM to be accessible over the internet through a load balancer, the VM itself must have a public IP address.
* In this case, the health check for the VM target is failing and the DNS returns a " NOT Found " message because web-1 does not have a public IP assigned.
* Without a public IP, the load balancer cannot route traffic to web-1 from the internet.
* Assigning a public IP to web-1 ensures that the VM can be accessed via the load balancer, resolving the connectivity issue.
Refer to the AWS documentation on network load balancers and public IP assignments, and Nutanix documentation on VM network configurations.
質問 # 67
An administrator is creating and destroying multiple clusters daily for a test/dev environment. The administrator wants ensure that every NC2 on AWS cluster deployed will allow full access from the on-premises CVM subnet.
What is most-efficient way to achive this?
- A. Modify the UVM Network Security Group of each cluster by setting the outbound allow address of the on-premises subnet.
- B. Modify the UVM Network Security Group of each cluster by setting the inbound allow address of the on-premises subnet.
- C. Create a Custom AWS Network Security Group using a key value of tag:nutanix:clusters:external and set the inbound allow address of the on-premises subnet.
正解:C
解説:
D/ Create a Custom AWS Network Security Group using a key of tag:nutanix: clusters:external:cluster-uuid and set the value of the UUID for each deployed cluster. Set the inbound allow address of the on-premises subnet.
To ensure that every NC2 on AWS cluster deployed allows full access from the on-premises CVM subnet efficiently, the administrator should create a custom AWS Network Security Group.
Use a key value of tag:nutanix:clusters:external for the security group, and set the inbound allow address to the on-premises subnet.
This approach leverages AWS tags to manage security group rules dynamically and ensures that the necessary access permissions are applied automatically to all clusters with the specified tag.
This method reduces the need for manual configuration of each cluster's security group, streamlining the process for a test/dev environment where clusters are frequently created and destroyed.
Reference:
Refer to the AWS documentation on Network Security Groups and Nutanix documentation on best practices for securing NC2 clusters.
質問 # 68
An administrator is tasked with deploying a VM in an NC2 cluster on AWS that needs to by accessed by resources within the on-premises datacenter.
The cluster has the following characteristics:
* 8 nodes
* Resides in the us-east-1a Availability Zone
* Contains 13 Subnets
* Has access to a Direct Connect connection
* Subnet that the User VM (UVM) is being deployed to:UserVM_subnet
There are multiple VMs within the cluster and the UserVM_subnet has access to the on-premises resources.
The administrator deploys the machine, but communication is not possible.
What is the most likely resolution for this situation?
- A. The AWS User Management Security Group requires the new application's ports adding to and traffic
- B. The AWS IGW requires the new application's ports adding to inbound traffic.
- C. The AWS Internal Management Security Group requires the new application's ports adding to outbound traffic.
- D. The AWS UVM Security Group requires the new application's ports adding to inbound traffic.
正解:D
解説:
For a VM deployed in an NC2 cluster on AWS to be accessed by resources within the on-premises datacenter, the security group associated with the User VM (UVM) subnet must allow inbound traffic on the specific ports required by the application.
If the security group rules do not permit inbound traffic on these ports, the communication will fail, even if other network configurations are correct.
The administrator should ensure that the UVM Security Group includes rules to allow inbound traffic for the application's required ports, facilitating proper communication between the VM and on-premises resources.
Reference:
Refer to the AWS documentation on security group configurations and Nutanix NC2 documentation for details on configuring network access and security group rules.
質問 # 69
A company has a large scale AWS deployment and has just finished installing their first NC2 on AWS cluster. The new cluster is now running workloads in production.
The cluster is configured with:
* 16 Nodes
* 8 Subnets
* 200 User VMs per subnet
* Nutanix Files
An administrator has been tasked with installing an EC2 instance on one of the subnets that is also used by the Nutanix, When the EC2 instance is powered on, an IP conflict occurs.
What action should the administrator take to resolve this issue?
- A. The IP address used by the NC2 VM should be blocked /excluded from EC2.
- B. The Instance Metadata of the NC2 instance needs to have the address reserved.
- C. The IP address used by the EC2 instance should be blocked / excluded from IPAM.
- D. Assign an elastic IP to the EC2 instance and reboot.
正解:A
解説:
To resolve the IP conflict issue when an EC2 instance is powered on in a subnet also used by Nutanix NC2, the administrator should block or exclude the IP address used by the NC2 VM from being assigned to EC2 instances. This can be done by configuring the IP address management (IPAM) settings to ensure that the specific IP addresses allocated to the NC2 VMs are not used by EC2 instances, preventing IP conflicts and ensuring smooth operation of both environments.
Nutanix Cloud Clusters on AWS Deployment Guide
Nutanix Support and Insights
質問 # 70
An administrator plans to configure Multicloud Snapshot Technology (MST) based Disaster Recovery (DR).
Which two options are valid limitations of MST DR? (Choose two.)
- A. MST can be configured when Prism Central with synchronous replication or AHV Metro is configured.
- B. The Zero Compute configuration does not support an automated failover recovery plan.
- C. Both MST DR and Cluster Protect features can be configured together.
- D. Only AHV VMs are protected with MST. ESXi VMs are currently not supported.
正解:C、D
解説:
Multicloud Snapshot Technology (MST)provides a cost-effective DR solution by offloading snapshots to cloud storage, but it has specific architectural limitations. First, it is currently limited to theAHV hypervisor; workloads running on ESXi are not supported for MST-based protection. Second, Nutanix allows for the simultaneous use of multiple protection layers; specifically,MST DR and Cluster Protectfeatures can be configured together to provide both local and remote resilience. It is also important to note that MST is designed for asynchronous recovery and is not compatible with Zero-RPO solutions like synchronous replication or AHV Metro at this time. Understanding these hypervisor and configuration constraints is essential when designing a disaster recovery strategy that relies on cloud object storage.
質問 # 71
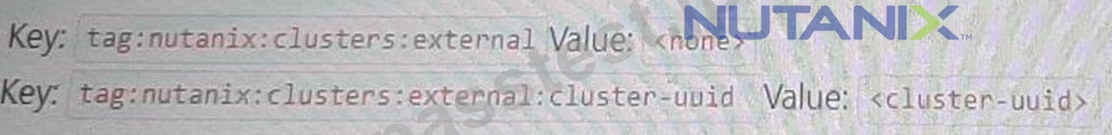
An administrator needs to allow wide open access to one particular NC2 AWS cluster from an on-premises subnet of 10.19.160.0/24.
What is the proper Custom Security Group formatting to satisfy this task?
- A.
- B.
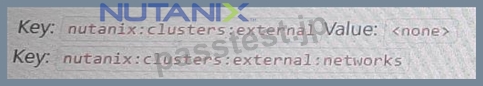
- C.
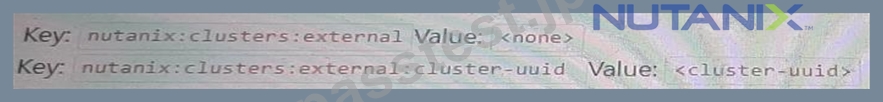
- D.
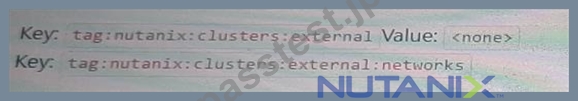
正解:C
解説:
To allow wide open access to a particular NC2 AWS cluster from an on-premises subnet (10.19.160.0/24), the proper Custom Security Group formatting needs to include the necessary tags that specify the external cluster UUID and the networks allowed.
Custom Security Group Configuration:
The configuration should include tags to identify the cluster and the networks that should be granted access.
Key: nutanix:clusters
Key: nutanix:clusters:external
Value: <cluster-uuid>
Explanation of Choice:
Option B includes the necessary tags and values, ensuring that the specific cluster UUID is recognized and the on-premises subnet (10.19.160.0/24) can communicate with the NC2 cluster.
Security Group Tags:
nutanix:clusters:external - Identifies the cluster as external.
nutanix:clusters:external:cluster-uuid - Specifies the unique identifier for the cluster, enabling proper traffic routing and access.
Reference:
Nutanix Cloud Clusters on AWS Administration Guide
AWS Security Group Documentation
Nutanix Best Practices for Custom Security Group Configuration
質問 # 72
......
合格させるNutanix NCP-CI-AWSプレミアムお試しセットテストエンジンPDFで無料問題集セット:https://www.passtest.jp/Nutanix/NCP-CI-AWS-shiken.html
NCP-CI-AWS試験情報と無料練習テスト:https://drive.google.com/open?id=1N5awDcufdCLrg_eBQ-Sy9gayIvmAAsyd