

PassTest NCP-CI-AWS問題集PDFで100%合格保証付き
NCP-CI-AWSブレーン問題集でリアル試験最新問題2025年07月23日には77問題
質問 # 33
During the recovery of entities protected by Cluster Project, an administrator discovers that the recovery plan is not executing correctly because it exceeds the number of supported entities.
How many entities can be recovered using a Single recovery plan?
- A. 0
- B. 1
- C. 2
- D. 3
正解:C
解説:
The Nutanix disaster recovery capabilities include recovery plans that define how entities are recovered in the event of a failure. There is a limit to the number of entities that can be managed within a single recovery plan.
Entity Limit:
According to Nutanix documentation, the maximum number of entities that can be recovered using a single recovery plan is 300. Exceeding this limit will cause issues during the execution of the recovery plan.
Impact of Exceeding the Limit:
If the number of entities in a recovery plan exceeds the supported limit, the recovery process may fail or not execute correctly, as observed in the scenario.
Reference:
Nutanix Cloud Clusters on AWS Administration Guide
Nutanix Disaster Recovery Best Practices Documentation
質問 # 34
A company wants to start using Nutanix Cloud Clusters (NC2) in AWS. The company has large spend commitments as part of an AWS Enterprise Discount Program (EDP) totaling $15 million.
What approach should the administrator take to ensure that Nutanix licensing costs to the EDP commitment?
- A. Leverage existing Nutanix licenses.
- B. Request a trial license directly from Nutanix
- C. Purchase Nutanix licenses directly from Nutanix and contact AWS support.
- D. Purchase Nutaniz licenses through the AWS Marketplace.
正解:D
解説:
Given the company's large spend commitments as part of an AWS Enterprise Discount Program (EDP) totaling $15 million, purchasing Nutanix licenses through the AWS Marketplace ensures that the costs contribute to the EDP commitment.
This approach integrates the Nutanix license costs into the overall AWS spend, thereby maximizing the benefits of the EDP.
Purchasing directly from Nutanix or leveraging existing licenses might not count towards the AWS EDP commitment, and trial licenses are typically for evaluation purposes and do not contribute to the committed spend.
Reference:
Refer to the Nutanix and AWS documentation on licensing and marketplace purchases, and EDP program details.
質問 # 35
The cluster is configured as follows:
* 8 nodes
* Prism Central Deployed
* Files Deployed
Following the deployment, the administrator experiences network connectivity issues.
Which reason explains the connectivity issues?
- A. The 192.168.5.0/24 range does not have enough IP addresses available.
- B. The 192.168.5.0/24 range is not a valid CIDR range.
- C. The 192.168.5.0/24 range is reserved by IANA,
- D. The 192.168.5.0/24 range is reserved for internal cluster usage.
正解:D
解説:
The 192.168.5.0/24 range is often reserved for internal cluster communication within Nutanix deployments.
Using this CIDR range for other purposes could lead to network conflicts and connectivity issues, as it might interfere with the internal operations and communication channels of the Nutanix cluster.
Ensuring that the CIDR range is not overlapping with any reserved ranges is crucial for maintaining proper network connectivity and cluster functionality.
Reference:
Refer to the Nutanix documentation on network configuration and best practices for NC2 deployments to confirm reserved IP ranges and their appropriate use.
質問 # 36
An administrator is deploying an NC2 cluster into an existing AWS VPC.
The cluster deployment fails, with the following error message:
Why has the deployment failed?
- A. Outbound Internet access is not configured on the VPC.
- B. The administrator has not configured the Security Group to manage the shared subnet.
- C. The administrator has not created the necessary Security Group.
- D. Shared subnets are not supported for Nutanix clusters.
正解:C
解説:
The administrator has not created the necessary Security Group:
The error message indicates that the creation of network interfaces in a shared subnet requires specifying a security group. This means that the necessary security group has not been created or assigned to the network interfaces.
Creating the appropriate security group and ensuring it is associated with the network interfaces during cluster deployment should resolve this issue.
Reference:
Refer to AWS documentation on security groups and network interface configuration and Nutanix documentation on prerequisites for deploying NC2 clusters in an existing AWS VPC.
質問 # 37
An administrator is tasked with enabling inbound internet access to two Virtual Servers in an NC2 cluster on AWS for the HTTPs protocol.
The cluster is configured with:
* 8 nodes
* Prism Central
* 3 x User VM subnets
All subnets have been configured and can communicate with Internet-based resources as well as on-premises servers. The company d to allow Internet access, so the administrator must implement an AWS solution.
Which approach will enable the necessary communication?
- A. Create a AWS Network Load Balancer, configure the listener TCP port as 80, create a target group and register the servers as targets.
- B. Create a AWS Network Load Balancer, configure the listener TCP port as 443, create a target group and register an HP as the endpoint.
- C. Create a WS Network Load Balancer, configure the listener TCP port as 80, create a target groud and register the servers as the endpoint
- D. Create a AWS Network Load Balancer, configure the lister TCP port as 433, create a target group and register an EIP as the Endpoint.
正解:B
解説:
To enable inbound internet access to Virtual Servers in an NC2 cluster on AWS for the HTTPS protocol, the administrator should use an AWS Network Load Balancer (NLB).
Configure the NLB listener to listen on TCP port 443, which is the standard port for HTTPS traffic.
Create a target group in AWS, and register the servers (Virtual Servers in the NC2 cluster) as targets within this group.
Ensure the NLB is properly configured with an Elastic IP (EIP) if required, to provide a static IP address for the load balancer.
Verify that the security groups and network ACLs associated with the load balancer and the target group allow inbound traffic on port 443.
Reference:
Refer to AWS documentation on Network Load Balancers and Nutanix NC2 on AWS integration guides for step-by-step instructions on setting up and configuring the necessary components for enabling HTTPS access.
質問 # 38
An administrator has deployed NC2 on AWS. The cluster deployment completed successfully.
After deployment, the administrator created a subnet in AWS, added it as a network in Prism Element, deployed Prism Central using the newly-configured network, and registered the cloud cluster with it.
The on-premises network and AWS are connected via a Site-to-Site VPN. Cluster nodes, CVM, and Prism Central can communicate with each other, but cannot be accessed from the on-premises network.
What two issues might be the cause of this problem? (Choose two.)
- A. The AWS VPC traffic is blocked by a firewall in the on-premises network.
- B. Traffic from the on-premises network is not permitted by VM and Management security groups.
- C. The AHV firewall is blocking traffic from the on-premises network.
- D. AWS Direct Connect must be used to establish connection between AWS and on-premises
正解:A、B
解説:
Traffic from the on-premises network is not permitted by VM and Management security groups:
Ensure that the security groups assigned to the VMs and management interfaces in AWS allow inbound traffic from the on-premises network. Without appropriate security group rules, the traffic will be blocked.
The AWS VPC traffic is blocked by a firewall in the on-premises network:
Check if the firewall on the on-premises network is configured to allow traffic from the AWS VPC. Firewalls may have restrictive rules that block incoming traffic, preventing communication.
Reference:
Refer to AWS documentation on security groups and firewalls and Nutanix documentation on configuring networking for NC2 clusters.
質問 # 39
Which entity should be contacted for cloud hardware supported (EC2 instances, VPC, etc) related to NC2?
- A. Public Cloud Vendor
- B. Internal IT Operations team
- C. Nutanix
- D. Partner
正解:A
解説:
For issues related to cloud hardware support such as EC2 instances, VPC, etc., the public cloud vendor (AWS in this case) should be contacted. AWS provides support and documentation for their infrastructure and services, ensuring that users can get assistance for any hardware or cloud-specific queries.
Reference:
Nutanix Support & Insights
質問 # 40
An administrator has noticed the company's NC2 free trial expired 60 days ago.
What should the administrator do to continue using all of the NC2 features on existing clusters?
- A. Switch to a paid subscription plan.
- B. Contact Nutanix support to redeploy the cluster.
- C. Contact the AWS cloud vendor.
- D. Nothing. The clusters will have full feature support.
正解:A
解説:
After the NC2 free trial expires, to continue using all features of NC2 on existing clusters, the administrator needs to switch to a paid subscription plan.
A paid subscription ensures uninterrupted access to the full range of features and support for NC2 clusters.
Without switching to a paid plan, the features might be limited, and support may not be available, impacting the cluster's operations and management.
Reference:
Refer to the Nutanix billing and subscription documentation for details on switching from a trial to a paid plan and the benefits associated with paid subscriptions.
質問 # 41
An administrator is investigating reports of network congestion on their NC2 deployment.
As part of the investigation, a packet capture is taken from a group of user VMs. During the analysis of the packet capture, it is observed that user VMs are receiving multicast traffic unexpectedly.
What action should the administrator take to resolve the issue?
- A. Disable DHCP snooping on the upstream network
- B. Disable IGMP snooping on the AHV hosts
- C. Enable DHCP snooping on the upstream network
- D. Enable IGMP snooping on the AHV hosts
正解:D
解説:
Enable IGMP snooping on the AHV hosts:
IGMP (Internet Group Management Protocol) snooping is a feature that listens to IGMP traffic between hosts and routers. By enabling IGMP snooping on the AHV (Acropolis Hypervisor) hosts, the switch can intelligently forward multicast traffic only to the ports that have requested it.
This reduces unnecessary multicast traffic on the network and prevents congestion by ensuring that multicast packets are only delivered to the appropriate endpoints.
Reference:
Refer to the Nutanix documentation on network configuration and best practices for managing multicast traffic.
質問 # 42
An administrator needs to backup Prism Central configuration data to an Amazon S3 bucket.
Which pcdr-cli command parameters is needed to satisfy this task?
- A. deployment-info
- B. protect
- C. list-protection-targets
- D. recover
正解:B
解説:
To backup Prism Central configuration data to an Amazon S3 bucket, the pcdr-cli command with the protect parameter is used. This parameter is specifically designed for creating protection policies and backing up Prism Central data.
Reference:
Nutanix Prism Central Documentation
Nutanix pcdr-cli Command Reference
質問 # 43
A company has just adopted Nutanix as their technology of choice and is preparing to deploy Nutanix Cloud Clusters (NC2).
Which step must be taken first to again access to the CN2 console?
- A. Create a My Nutanix account
- B. Open a support case with Nutanix.
- C. Start a free trial via Billing Portal.
- D. Navigate to cloud.nutanix.com
正解:A
解説:
Before accessing the Nutanix Cloud Clusters (NC2) console, the first step is to create a My Nutanix account.
This account serves as the primary gateway for managing and accessing Nutanix services, including NC2.
Once the account is created, users can log in to the Nutanix portal, where they can manage their subscriptions, start trials, and access various Nutanix services, including the NC2 console.
Reference:
Refer to the Nutanix documentation on getting started with NC2 and the My Nutanix account creation process.
質問 # 44
An administrator needs to create user VM subnets for multiple NC2 clusters in AWS.
What would be the best approach to take?
- A. Create guest-VM subnets to be shared by all clusters.
- B. Create guest-VM subnets for each cluster.
- C. Use the cluster management subnet dedicated to each cluster.
- D. Create guest-VM VNets for each cluster.
正解:B
解説:
When creating user VM subnets for multiple NC2 clusters in AWS, the best approach is to create guest-VM subnets for each cluster. This ensures that each cluster has its own dedicated subnets, which simplifies network management and avoids potential IP conflicts.
Advantages of Dedicated Subnets:
Isolation: Each cluster operates in its own subnet, providing better isolation and security.
Management: Easier to manage and troubleshoot network issues when each cluster has its own subnets.
Scalability: More scalable as each subnet can be managed and expanded independently.
Steps to Create Guest-VM Subnets:
Identify the IP range for each subnet.
In the AWS VPC console, create a new subnet for each cluster using the identified IP ranges.
Associate the new subnets with the respective clusters during or after the cluster deployment process.
Why Not Shared Subnets:
Shared subnets could lead to IP conflicts and make network management more complex, especially as the number of clusters grows.
Reference:
Nutanix Cloud Clusters on AWS Administration Guide
AWS VPC Subnet Creation Documentation
質問 # 45
An administrator has been tasked with deploying a new production NC2 cluster on AWS and is studying the deployment..
AWS supports EC2 bare-metal instances in regions with at least how many partitions?
- A. 0
- B. 1
- C. 2
- D. 3
正解:B
解説:
AWS supports EC2 bare-metal instances in regions with at least 3 partitions. Partitions in AWS provide high availability and fault tolerance by distributing instances across different hardware to minimize the impact of hardware failures.
Reference:
AWS EC2 Bare Metal Instances Documentation
AWS Regions and Availability Zones
質問 # 46
A company has purchased Nutanix AOS Pro licensing.
Which add-on products are available with this license tier in the AWS cluster deployment wizard?
- A. EUC
- B. Nus
- C. Files, Advanced Replication, and DARE
- D. Self-Service and Cost Governance
正解:C
解説:
With the Nutanix AOS Pro licensing, several advanced features and add-on products become available. Specifically, in the AWS cluster deployment wizard, the following add-ons are available:
Files:
Nutanix Files provides a software-defined, scale-out file storage solution that simplifies the management and scaling of unstructured data.
Advanced Replication:
Advanced Replication features in Nutanix include synchronous and asynchronous replication capabilities, allowing for robust disaster recovery and data protection solutions.
DARE (Data-At-Rest Encryption):
DARE ensures that all data stored on Nutanix clusters is encrypted, providing a higher level of security for sensitive information.
These features are included in the AOS Pro licensing tier, offering enhanced data management, protection, and security capabilities.
Reference:
Nutanix Licensing Guide
Nutanix Cloud Clusters on AWS Administration Guide
Nutanix Best Practices for Advanced Features
質問 # 47
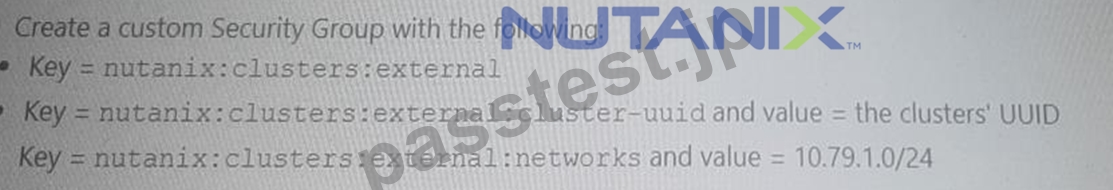
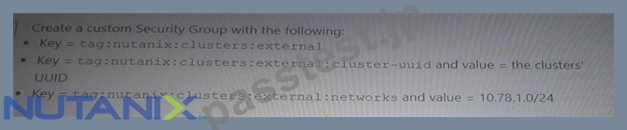
An administrator has deployed an NC2 on AWS cluster that is running mixed workloads. Multiple SQL database are running on the NC2 cluster using a native subnet of 10.78.1.0/24.
The administrator wants to ensure only application servers from source subnet 10.79.1.0/24 that reside outside of the NC2 cluster can access the databases.
Which two actions will help the administrator most securely achieve this? (Choose two.)
- A.
- B.

- C.

- D.
正解:A、D
解説:
To ensure that only application servers from the source subnet 10.79.1.0/24 can access the SQL databases running on the NC2 cluster in the subnet 10.78.1.0/24, the administrator can take the following actions:
Option A: Create a custom Security Group with the following rules:
Key = tag:nutanix:clusters
Key = tag:nutanix:clusters:external
and value = the clusters' UUID
Key = tag:nutanix:clusters:external
and value = 10.78.1.0/24
Option D: Create a custom Security Group with the following:
Key = nutanix:clusters
Key = nutanix:clusters:external
and value = the clusters' UUID
Key = nutanix:clusters:external
and value = 10.79.1.0/24
These actions help create security rules that restrict access to the databases only from the specified source subnet, ensuring secure and controlled access.
Reference:
Nutanix Cloud Clusters on AWS Administration
AWS Security Groups Documentation
質問 # 48
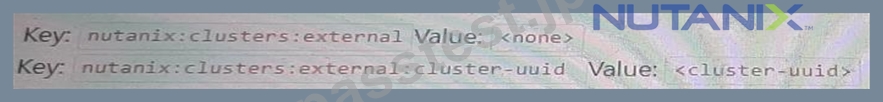
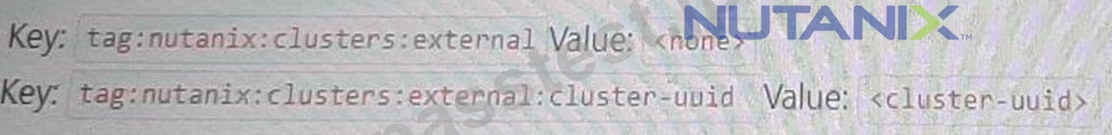
An administrator needs to allow wide open access to one particular NC2 AWS cluster from an on-premises subnet of 10.19.160.0/24.
What is the proper Custom Security Group formatting to satisfy this task?
- A.
- B.
- C.
- D.
正解:A
解説:
To allow wide open access to a particular NC2 AWS cluster from an on-premises subnet (10.19.160.0/24), the proper Custom Security Group formatting needs to include the necessary tags that specify the external cluster UUID and the networks allowed.
Custom Security Group Configuration:
The configuration should include tags to identify the cluster and the networks that should be granted access.
Key: nutanix:clusters
Key: nutanix:clusters:external
Value: <cluster-uuid>
Explanation of Choice:
Option B includes the necessary tags and values, ensuring that the specific cluster UUID is recognized and the on-premises subnet (10.19.160.0/24) can communicate with the NC2 cluster.
Security Group Tags:
nutanix:clusters:external - Identifies the cluster as external.
nutanix:clusters:external:cluster-uuid - Specifies the unique identifier for the cluster, enabling proper traffic routing and access.
Reference:
Nutanix Cloud Clusters on AWS Administration Guide
AWS Security Group Documentation
Nutanix Best Practices for Custom Security Group Configuration
質問 # 49
Which NC2 user role will allow full access to clusters created within an organization?
- A. Organization Security Administrator
- B. Organization Administrator
- C. Cluster Super Admin
- D. Cluster Administrator
正解:B
解説:
In Nutanix Cloud Integration with AWS, specifically version 6.7, the role that allows full access to clusters created within an organization is the Organization Administrator.
The Organization Administrator role has the highest level of privileges within an organization, enabling the user to manage all aspects of the clusters, including creation, modification, and deletion.
This role is designed to oversee and control the entire organization's resources, ensuring comprehensive management capabilities over all clusters and associated resources.
Reference:
Refer to the Nutanix documentation on roles and permissions for NC2 on AWS for further details.
質問 # 50
An administrator is planning a new NC2 on AWS deployment. The workload VMs to be deployed on the new cluster have low storage and memory, but high CPU frequency (>3.0 GHz) requirements.
The administrate! has also been tasked with ensuring that the cluster nodes have the lowest number of CPU cores to reduce application licensing requirements.
Which node type will satisfy this new deployment?
- A. i4i.metal
- B. zld.metal
- C. m5d.metal
- D. i3.metal
正解:D
解説:
For a new NC2 on AWS deployment where workload VMs have low storage and memory requirements but high CPU frequency (>3.0 GHz) requirements, and the goal is to minimize the number of CPU cores to reduce application licensing costs, the i3.metal instance type is the most suitable.
i3.metal:
High CPU Frequency: i3.metal instances offer high-frequency Intel Xeon processors (up to 3.1 GHz) which meet the high CPU frequency requirement.
Low Storage and Memory: These instances come with a balanced amount of storage and memory, suitable for workloads with low requirements in these areas.
Minimized CPU Cores: i3.metal instances have fewer CPU cores compared to other high-frequency instances like i4i.metal, making them ideal for minimizing application licensing costs.
Other Instance Types:
z1d.metal: While also offering high CPU frequency, these instances typically come with a higher core count and more memory, which may not be optimal for minimizing licensing costs.
i4i.metal: Designed for I/O intensive applications with higher core counts.
m5d.metal: Balanced instance type but with more cores and not as high CPU frequency as required.
Reference:
AWS EC2 Instance Types Documentation
Nutanix Cloud Clusters on AWS Administration Guide
Nutanix Best Practices for Instance Selection
質問 # 51
An administrator has recently deployed an NC2 on AWS cluster in the North Virginia region in availability zone us-east-1z. The clusters UUID is 0005F487-4962-91EA-4C98-C4284D123835.
The cluster is consuming IPs from a 10.78.2.0/24 range.
The AWS VPC has these available CIDR ranges:
* 70.73.0.0/16
* 10.79.107.0/24
* 10.0.0.0/22
The following subnets have been configured in the NC2 AWS VPC: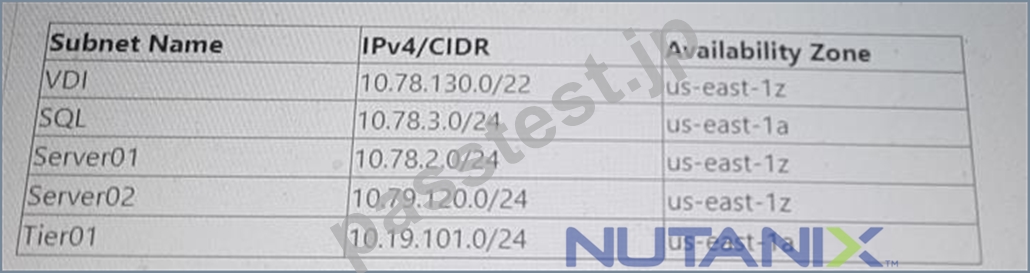
The following tags have been applied to a Custom Network Security Group: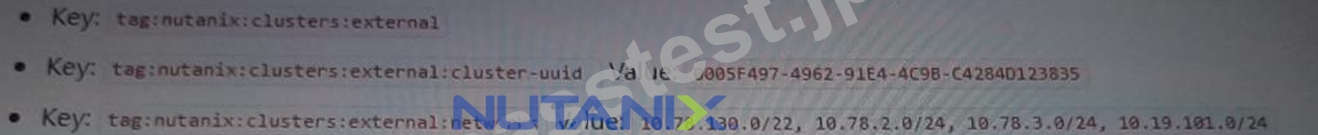
The Custom Network Security Group is allowing all inbound traffic from the 10.0.0.0/22 network. Which two subnets would be able to receive inbound traffic from AWS instances on a 10.0.0.0/22 network segment"? (Choose two.)
- A. Tier01
- B. SQL
- C. Server01
- D. VDl
正解:A、C
解説:
To determine which subnets would be able to receive inbound traffic from AWS instances on a 10.0.0.0/22 network segment, we need to look at the configured subnets and their CIDR ranges, as well as the custom network security group's inbound rules.
Available CIDR ranges in VPC:
70.73.0.0/16
10.79.107.0/24
10.0.0.0/22
Configured Subnets in NC2 AWS VPC:
VDI: 10.78.130.0/22
SQL: 10.78.3.0/24
Server01: 10.78.2.0/24
Server02: 10.79.120.0/24
Tier01: 10.19.101.0/24
Custom Network Security Group Inbound Rule:
Allows all inbound traffic from 10.0.0.0/22.
Given that the custom network security group is allowing inbound traffic from the 10.0.0.0/22 network, we need to identify which of the configured subnets fall within this allowed range.
Analysis:
The subnets 10.78.130.0/22, 10.78.3.0/24, 10.78.2.0/24, 10.79.120.0/24, and 10.19.101.0/24 do not overlap with 10.0.0.0/22. Therefore, none of these subnets would naturally fall within the 10.0.0.0/22 range directly.
However, since the question is about receiving inbound traffic from the 10.0.0.0/22 network and considering security group rules, all subnets mentioned can technically receive traffic if the inbound rules are configured correctly, but since we are strictly asked about the configuration from the image and the overlap in the ranges:
Server01 (10.78.2.0/24) and Tier01 (10.19.101.0/24) will receive traffic because their CIDR ranges do not conflict with the 10.0.0.0/22 range, thus allowing traffic without additional restrictions.
Reference:
Nutanix Clusters on AWS Administration Guide
AWS VPC and Subnet documentation
Network Security Group rules configuration in Nutanix documentation
質問 # 52
preparing the landing zone networking resources for a Nutanix cluster on AWS. The administrator has created a VPC with two private subnets: one for cluster management and one for user VMs.
What additional subnet must the administrator create?
- A. Private subnet for Prism Central
- B. Public subnet for S3 access
- C. Private subnet for VPN gateway
- D. Public subnet for Internet access
正解:D
解説:
When setting up a landing zone for Nutanix clusters on AWS, having only private subnets for cluster management and user VMs is not sufficient for full cluster functionality. Nutanix clusters often need to communicate with the internet for updates, patches, and other cloud services.
VPC Configuration:
The VPC already has two private subnets (one for cluster management and one for user VMs).
Additional Requirements:
To access public services like S3 or for the cluster nodes to reach Nutanix services for updates, a public subnet is essential.
Why Public Subnet for Internet Access?:
A public subnet allows resources within it to communicate directly with the internet, which is necessary for accessing Nutanix's update servers, applying patches, and other maintenance tasks.
This subnet typically includes an internet gateway, enabling instances in the public subnet to receive and send traffic directly to the internet.
Reference:
Nutanix Cloud Clusters on AWS Administration Guide
AWS Networking Best Practices
Nutanix Networking and Subnet Configuration Guidelines
質問 # 53
......
NCP-CI-AWS問題集には100%厳密検証された問題と解答で合格保証付きもしくは全額返金:https://www.passtest.jp/Nutanix/NCP-CI-AWS-shiken.html
最新NCP-CI-AWSPDF問題集リアル無料テスト本日更新です:https://drive.google.com/open?id=1N5awDcufdCLrg_eBQ-Sy9gayIvmAAsyd