

更新された2023年10月18日検証済み!PCNSA日本語問題集と解答で100%合格できる
2023年最新のの問題PCNSA日本語問題集を試そう!更新されたPalo Alto Networks試験合格させます
質問 # 37
サイバー攻撃のライフサイクルのどの段階で、スピアフィッシングリンク、未知の電子メール、および危険なWebサイトについてユーザーに継続的な教育を提供することが重要になりますか?
- A. 配達
- B. インストール
- C. 搾取
- D. 偵察
正解:A
解説:
Weaponization and Delivery: Attackers will then determine which methods to use in order to deliver malicious payloads. Some of the methods they might utilize are automated tools, such as exploit kits, spear phishing attacks with malicious links, or attachments and malvertizing. Gain full visibility into all traffic, including SSL, and block high-risk applications. Extend those protections to remote and mobile devices.
Protect against perimeter breaches by blocking malicious or risky websites through URL filtering. Block known exploits, malware and inbound command-and- control communications using multiple threat prevention disciplines, including IPS, anti-malware, anti-CnC, DNS monitoring and sinkholing, and file and content blocking.
Detect unknown malware and automatically deliver protections globally to thwart new attacks. Provide ongoing education to users on spear phishing links, unknown emails, risky websites, etc.
https://www.paloaltonetworks.com/cyberpedia/how-to-break-the-cyber-attack-lifecycle
質問 # 38
管理者は、バッファ オーバーフローや不正なコード実行などの受信脅威から保護したいと考えています。
どのセキュリティ プロファイルを使用する必要がありますか?
- A. ウイルス対策
- B. URLフィルタリング
- C. 脆弱性保護
- D. スパイウェア対策
正解:D
質問 # 39
パケットの送信元IPアドレスと宛先IPアドレスの個々の組み合わせに基づいて、ICMPフラッドに対して最良の保護を提供するセキュリティプロファイルはどれですか。
- A. パケットバッファリング
- B. スパイウェア対策
- C. URLフィルタリング
- D. DoS保護
正解:D
質問 # 40
内部ゾーンと外部ゾーンの間、内部ゾーン内、および外部ゾーン内のトラフィックに一致するセキュリティルールのタイプはどれですか。
- A. ゾーン内
- B. ユニバーサル
- C. ゾーン間
- D. グローバル
正解:B
解説:
Explanation
References: https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClomCAC
質問 # 41
セキュリティ管理者が新しいアプリケーションシグニチャに一致するセキュリティポリシールールをプレビューできるのは何ですか?
- A. 動的更新-ポリシーの確認
- B. ポリシーオプティマイザー-新しいアプリビューアー
- C. 動的更新-レビューアプリ
- D. リリースノートを確認する
正解:A
解説:
https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-admin/app-id/manage-new-app-ids-introduced-in-content-releases/review-new-app-id-impact-on-existing-policy-rules
質問 # 42
表示されている2つの構成設定がデフォルトではありませんか? (2つ選択してください。)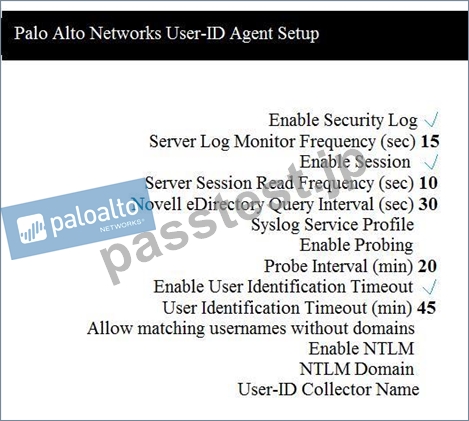
- A. セッションを有効にする
- B. サーバーログモニターの頻度(秒)
- C. セキュリティログを有効にする
- D. プロービングを有効にする
正解:A、B
質問 # 43
自動コミット回復機能の目的は何ですか?
- A. 変更後に Panorama への接続が失われたことをファイアウォールが認識した場合、ファイアウォール設定を元に戻します。
- B. Panorama 設定が最後に実行中の設定に正常に戻った後、設定ログが生成されます。
- C. パノラマ設定を元に戻します。
- D. Panorama からのプッシュ後に HA ピア間で HA 同期が自動的に行われます。
正解:A
質問 # 44
ドラッグアンドドロップの質問
次の手順を、パケット処理の最初から最後までの順序で実行します。
選択して配置: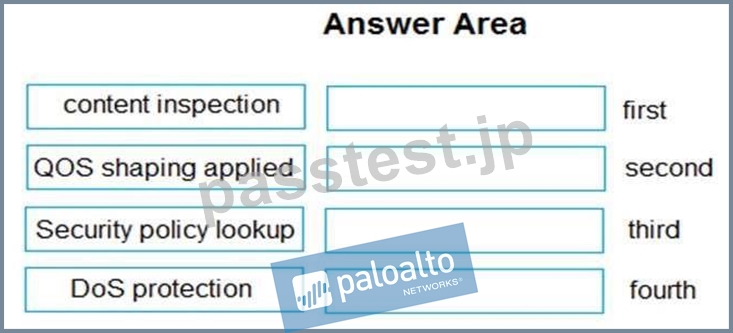
正解:
解説: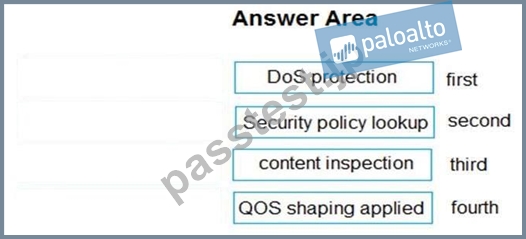
質問 # 45
動的ユーザー グループを作成するにはどうすればよいですか?
- A. ファイアウォール管理者の動的リストを作成します
- B. 異常なユーザーの動作と悪意のあるアクティビティの自動修復を提供する QoS ポリシーを作成します。
- C. 異常なユーザーの動作と悪意のあるアクティビティの自動サイズ設定を提供するポリシーを作成します
- D. 異常なユーザーの行動と悪意のあるアクティビティの自動修復を提供するポリシーを作成します
正解:D
解説:
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-new-features/user-id-features/dynamic-user-groups#:~:text=Dynamic%20user%20groups%20help%20you,activity%20while%20maintaining%20user%20visibility.
質問 # 46
ドラッグ アンド ドロップの質問
次のステップを、パケット処理操作の最初から最後までの順序で配置します。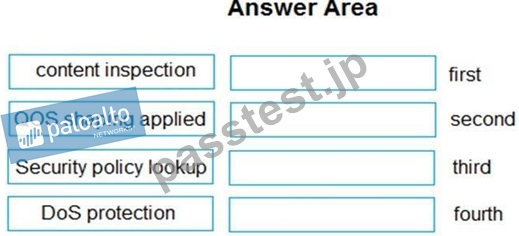
正解:
解説: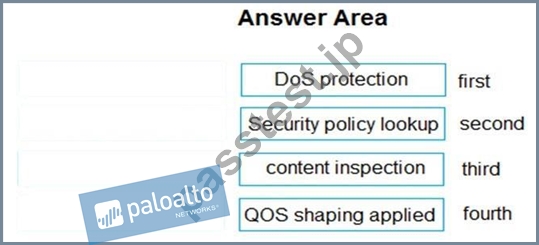
Explanation:
https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClVHCA0
質問 # 47
管理者は、メンテナンス ウィンドウ アクティビティの前に、実行コンフィギュレーションのみのバックアップを外部の場所に作成したいと考えています。[デバイス] > [セットアップ] > [操作] のどのコマンドが、この結果を達成するための最も運用効率の高い方法を提供しますか?
- A. デバイスの状態をエクスポート
- B. 候補設定を保存
- C. 名前付き構成スナップショットを保存
- D. 名前付き構成スナップショットのエクスポート
正解:C
解説:
Export Named Configuration Snapshot This option exports the current running configuration, a candidate configuration snapshot, or a previously imported configuration (candidate or running). The firewall exports the configuration as an XML file with the specified name. You can save the snapshot in any network location. These exports often are used as backups. These XML files also can be used as templates for building other firewall configurations.
質問 # 48
ドラッグアンドドロップの質問
パロアルトネットワークファイアウォールを使用して新しいセキュリティゾーンを作成するために必要な手順を注文します。
選択して配置: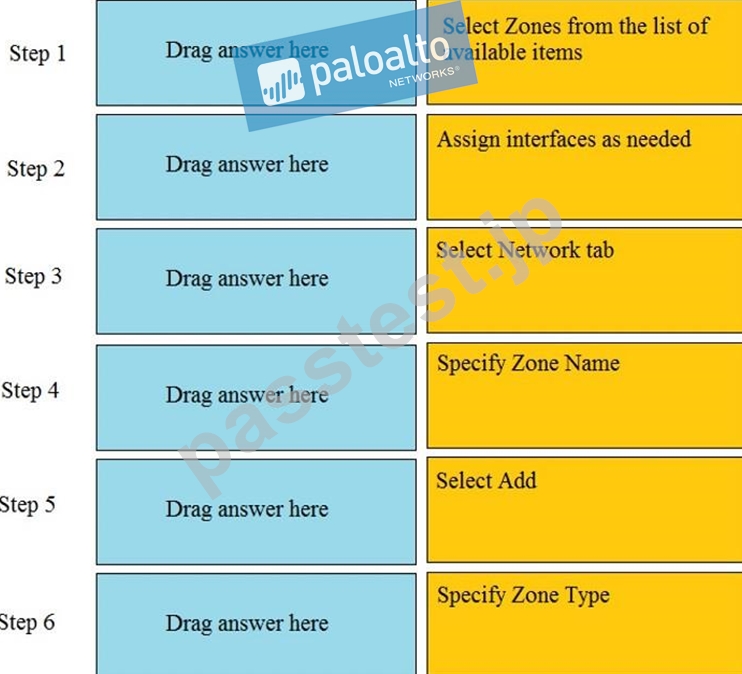
正解:
解説: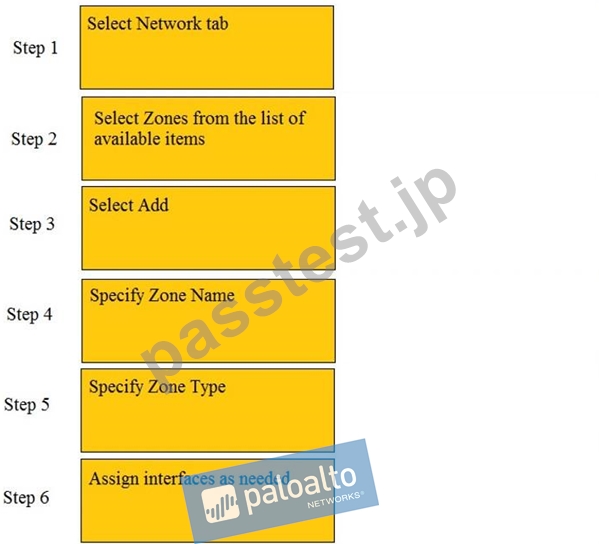
質問 # 49
表示されたセキュリティポリシールールに基づいて、sshはどのポートで許可されますか?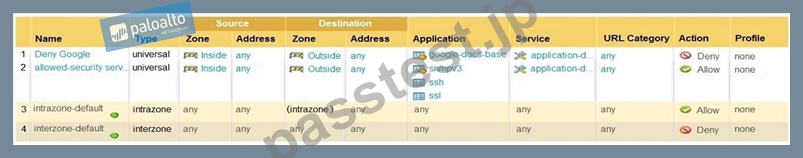
- A. 0
- B. 1
- C. 2
- D. 3
正解:C
質問 # 50
DNS 署名をチェックできるようにするには、どのセキュリティ プロファイルをセキュリティ ポリシーに追加する必要がありますか?
- A. ウイルス対策
- B. URLフィルタリング
- C. 脆弱性保護
- D. スパイウェア対策
正解:D
解説:
In addition, you can enable the DNS sinkholing action in Anti-Spyware profiles to enable the firewall to forge a response to a DNS query for a known malicious domain, causing the malicious domain name to resolve to an IP address that you define.
https://docs.paloaltonetworks.com/pan-os/11-0/pan-os-admin/policy/security-profiles
質問 # 51
管理者は、リストにエントリを手動で追加することにより、外部の動的リストに例外を実装しています。管理者は変更を保存したいと考えていますが、[OK] ボタンはグレー表示されています。
[OK] ボタンがグレー表示されている理由として考えられるものを 2 つ挙げてください。(2つ選んでください。)
- A. エントリにワイルドカードが含まれています。
- B. エントリが重複しています。
- C. エントリはリスト エントリと一致します。
- D. エントリがリスト エントリと一致しません。
正解:B、D
質問 # 52
権限を管理したり、ファイルの機密情報をスキャンしたりして、Dropbox や Salesforce などのクラウドベースのアプリケーションを保護するサービスはどれですか?
- A. オートフォーカス
- B. パリスマ SaaS
- C. 絞り
- D. グローバルプロテクト
正解:B
質問 # 53
管理者は、ベスト プラクティスに合わせてセキュリティ ポリシーを更新しています。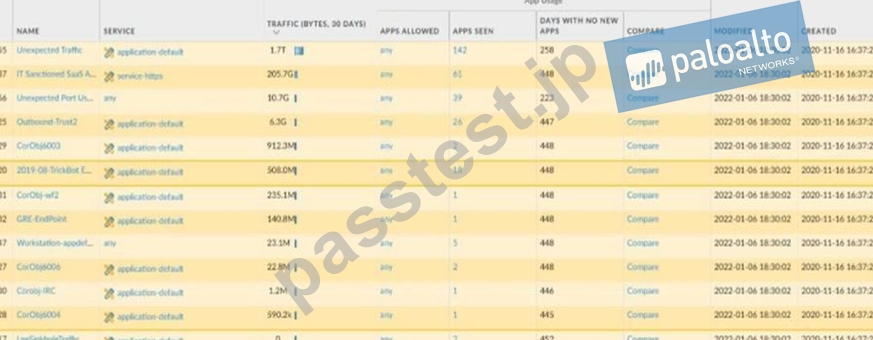
以下のスクリーンショットに示されているのは、どの Policy Optimizer 機能ですか?
- A. 未使用のアプリ
- B. 新しいアプリビューア
- C. アプリコントロールのないルール
- D. ルールの使用法 - 未使用
正解:C
解説:
https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-admin/app-id/security-policy-rule- optimization/migrate-port-based-to-app-id-based-security-policy-rules
質問 # 54
DNS シンクホールを有効にするには、どの 2 つのアドレスを予約する必要がありますか? (2つお選びください。)
- A. MAC
- B. メール
- C. IPv4
- D. IPv6
正解:C、D
解説:
https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClGECA0
質問 # 55
スクリーンショットを考えると、ログに記録されたトラフィックに関する2つの正しいステートメントは何ですか? (2つ選択してください。)
- A. Webセッションが復号化されました。
- B. Webセッションの復号化に失敗しました。
- C. トラフィックはセキュリティプロファイルによって拒否されました。
- D. トラフィックはURLフィルタリングによって拒否されました。
正解:A、D
質問 # 56
示されているグラフィックのどのデータプレーンプロセッサレイヤーが、パロアルトネットワークファイアウォールのスパイウェアおよび脆弱性の悪用に対して統一的なマッチングを提供していますか?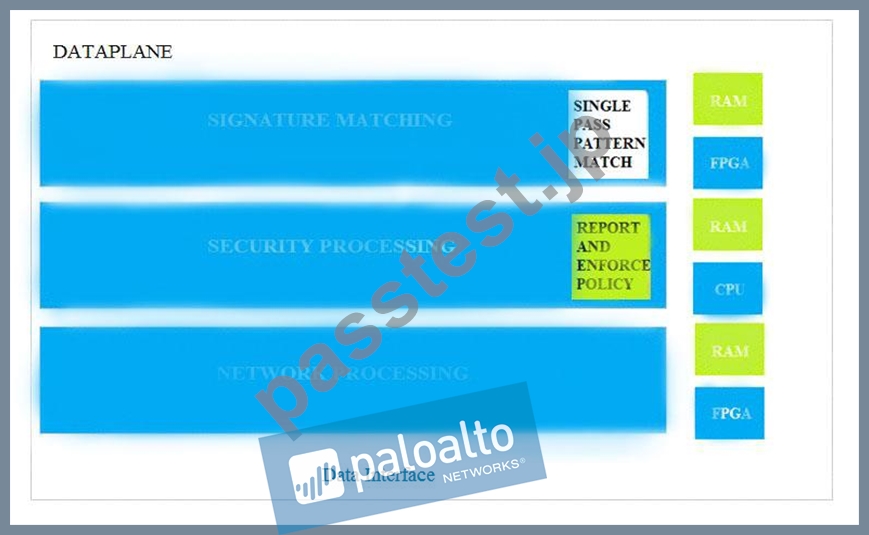
- A. セキュリティマッチング
- B. 署名照合
- C. ネットワーク処理
- D. セキュリティ処理
正解:B
質問 # 57
タイプIPワイルドカードマスクのアドレスオブジェクトは、構成のどの部分で参照できますか?
- A. NATアドレスプール
- B. ACCグローバルフィルター
- C. 外部動的リスト
- D. セキュリティポリシールール
正解:D
解説:
You can use an address object of type IP Wildcard Mask only in a Security policy rule.
https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-web-interface-help/objects/objects-addresses IP Wildcard Mask
--Enter an IP wildcard address in the format of an IPv4 address followed by a slash and a mask (which must begin with a zero); for example,
10.182.1.1/0.127.248.0. In the wildcard mask, a zero (0) bit indicates that the bit being compared must match the bit in the IP address that is covered by the 0. A one (1) bit in the mask is a wildcard bit, meaning the bit being compared need not match the bit in the IP address that is covered by the 1. Convert the IP address and the wildcard mask to binary. To illustrate the matching: on binary snippet 0011, a wildcard mask of 1010 results in four matches (0001, 0011, 1001, and 1011).
質問 # 58
PAN-OS 10.0のどのパスに、ポートベースのセキュリティポリシールールのリストが表示されますか?
- A. Policies> Security> Rule Usage> Port only specified
- B. Policies> Security> Rule Usage> Unused Apps
- C. Policies> Security> Rule Usage> Port-based Rules
- D. Policies> Security> Rule Usage> No App Specified
正解:C
質問 # 59
......
最新のPCNSA日本語試験問題集でPalo Alto Networksトレーニング試験には:https://www.passtest.jp/Palo-Alto-Networks/PCNSA-JPN-shiken.html