

PDF無料ダウンロードにはPCNSA日本語有効な練習テスト問題
PCNSA日本語テストエンジンお試しセット、PCNSA日本語問題集PDF
質問 # 160
セキュリティポリシールールまたはセキュリティプロファイルの操作を説明する3つのステートメントはどれですか。 (3つ選択してください)
- A. セキュリティポリシールールはセキュリティプロファイルに添付されます。
- B. セキュリティポリシールールは、トラフィックをブロックまたは許可できます。
- C. セキュリティプロファイルは、許可されたトラフィックでのみ使用する必要があります。
- D. セキュリティポリシールールはトラフィックを検査しますがブロックしません。
- E. セキュリティプロファイルはセキュリティポリシールールに添付されます。
正解:B、C、E
質問 # 161
Active Directory ユニバーサル グループでグループ マッピングを使用する場合、ユーザー ID を構成するときに何をする必要がありますか?
- A. ポート 636 で LDAPS を使用してドメイン コントローラーに接続するための RADIUS サーバー プロファイルを作成するか、
- B. ユーザーベースのセキュリティ ポリシーの主要従業員 ID 番号を構成します。
- C. ポート上でグローバル カタログ サーバーのルート ドメインに接続するための LDAP サーバー プロファイルを作成します。
SSL の場合は 3268 または 3269 - D. グループ マッピング キャッシュをクリアする頻度スケジュールを設定します。
正解:C
解説:
If you have Universal Groups, create an LDAP server profile to connect to the root domain of the Global Catalog server on port 3268 or 3269 for SSL, then create another LDAP server profile to connect to the root domain controllers on port 389. This helps ensure that users and group information is available for all domains and subdomains.
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/user-id/map-users-to-groups
質問 # 162
パロアルトネットワークファイアウォールのどの2つの認証方法が、役割ベースのアクセス制御の認証と承認をサポートしていますか? (2つ選択してください。)
- A. TACACS +
- B. SAML
- C. Kerberos
- D. LDAP
正解:A、B
解説:
Reference:
The administrative accounts are defined on an external SAML, TACACS+, or RADIUS server. The server performs both authentication and authorization. For authorization, you define Vendor-Specific Attributes (VSAs) on the TACACS+ or RADIUS server, or SAML attributes on the SAML server. PAN-OS maps the attributes to administrator roles, access domains, user groups, and virtual systems that you define on the firewall.
質問 # 163
Panorama で [未使用のアドレスとサービス オブジェクトをデバイスと共有] 設定を無効にすると何が実現できますか?
- A. アドレスおよびサービス オブジェクトのファイアウォールごとの容量を増加します。
- B. ファイアウォールにプッシュされるオブジェクトの数を減らします。
- C. HA ペア間の構成とセッションの同期時間を短縮します。
- D. ファイアウォールごとの構成バックアップのバックアップ容量を増やす
正解:B
質問 # 164
show securityポリシールールに基づいて、内部ゾーンから外部ゾーンへのすべてのFTPトラフィックを照合しますか?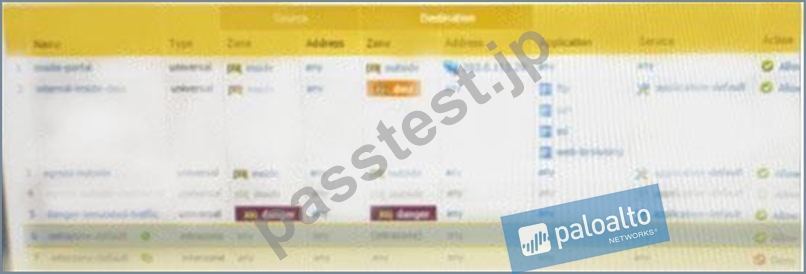
- A. 内部ポータル
- B. intercone-default
- C. internal-inside-dmz
- D. 外の入口
正解:B
質問 # 165
表示されている2つの構成設定がデフォルトではありませんか? (2つ選択してください。)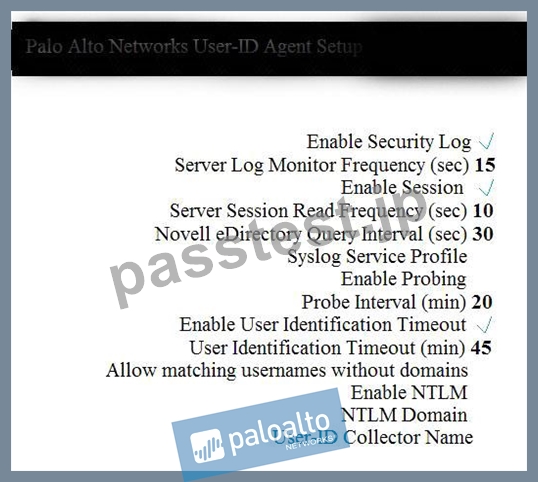
- A. サーバーログモニターの頻度(秒)
- B. セキュリティログを有効にする
- C. セッションを有効にする
- D. プロービングを有効にする
正解:A、C
質問 # 166
ファイアウォールで山火事の更新を利用できる頻度はどれくらいですか?
- A. 15分ごと
- B. 60分ごと
- C. 5分ごと
- D. 30分ごと
正解:C
解説:
WildFire Provides near real-time malware and antivirus signatures created as a result of the analysis done by the WildFire public cloud. WildFire signature updates are made available every five minutes. You can set the firewall to check for new updates as frequently as every minute to ensure that the firewall retrieves the latest WildFire signatures within a minute of availability.
Without the WildFire subscription, you must wait at least 24 hours for the signatures to be provided in the Antivirus update.
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/software-and-content- updates/dynamic-content-updates
質問 # 167
ドラッグアンドドロップの質問
次の手順を、パケット処理の最初から最後までの順序で実行します。
選択して配置:
正解:
解説: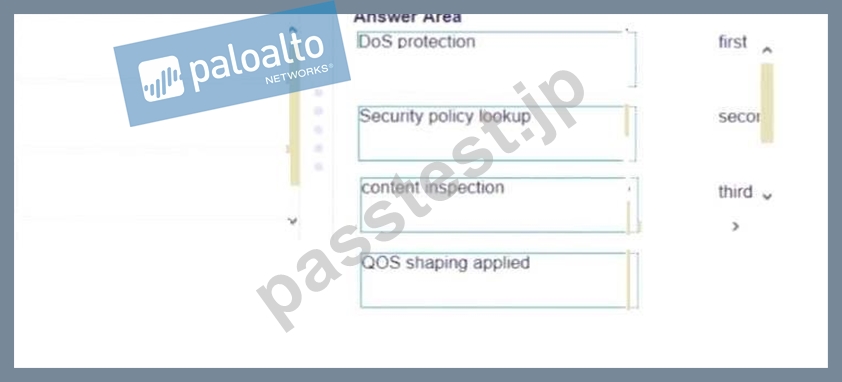
質問 # 168
Palo Alto Networks Security Operating Platform アーキテクチャをその説明と一致させてください。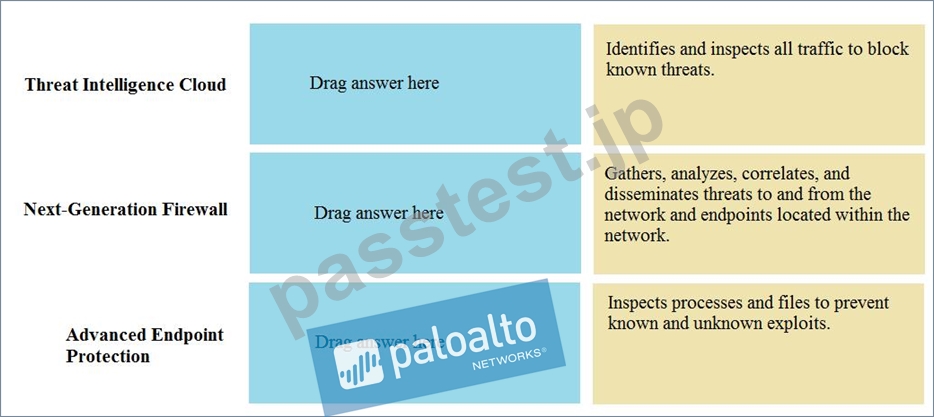
正解:
解説: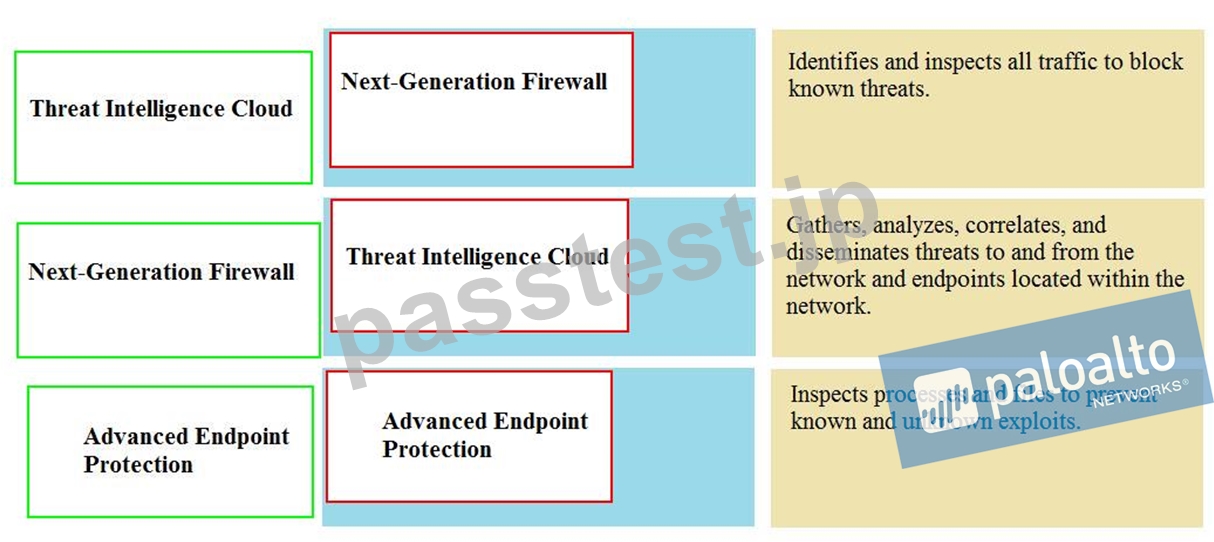
質問 # 169
2 種類の管理者アカウントとは何ですか? (2つお選びください。)
- A. スーパーユーザー
- B. 役割ベース
- C. ダイナミック
- D. ローカル
正解:B、C
解説:
https://docs.paloaltonetworks.com/pan-os/11-0/pan-os-admin/firewall-administration/manage- firewall-administrators/configure-administrative-accounts-and-authentication/configure-a-firewall- administrator-account
質問 # 170
カスタム アプリケーションが作成される 2 つの主な理由は何ですか? (2つお選びください。)
- A. ネットワーク上の不明なトラフィックを減らすため
- B. 類似したアプリケーションを視覚的にグループ化します。
- C. アプリケーションのデフォルトの分類を変更するには
- D. トラフィック ログ内の内部アプリケーションを正確に識別するため
正解:A、D
解説:
https://docs.paloaltonetworks.com/pan-os/11-0/pan-os-admin/app-id/use-application-objects-in-policy/create-a-c
質問 # 171
ユーザーがそのURLにアクセスしようとしたときにログエントリを生成しないURLプロファイリングアクションはどれですか。
- A. オーバーライド
- B. 続行
- C. ブロック
- D. 許可
正解:D
解説:
Allow traffic destined for that URL category; allowed traffic is not logged.
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/url-filtering/configure-url-filtering.html
質問 # 172
ネットワーク管理者は、ファイアウォールでゾーン内セキュリティ ポリシー ルールを作成しました。ソース ゾーンは IT に設定されました。財務、人事。
ルールが適用されるトラフィックの 2 つのタイプはどれですか? (2つ選んでください)
- A. ゾーン IT とゾーン Finance 間のトラフィック
- B. ゾーン IT 内のトラフィック
- C. ゾーン HR 内のトラフィック
- D. ゾーン Finance とゾーン HR 間のトラフィック
正解:B、C
質問 # 173
管理者が利用できない更新オプションはどれですか?
- A. 新しいウイルス対策署名
- B. 新しいアプリケーション署名
- C. 新しいURL
- D. 新しい悪意のあるドメイン
- E. 新しいスパイウェア通知
正解:C
質問 # 174
Cyber-Attack Lifecycleステージをその正しい説明に一致させます。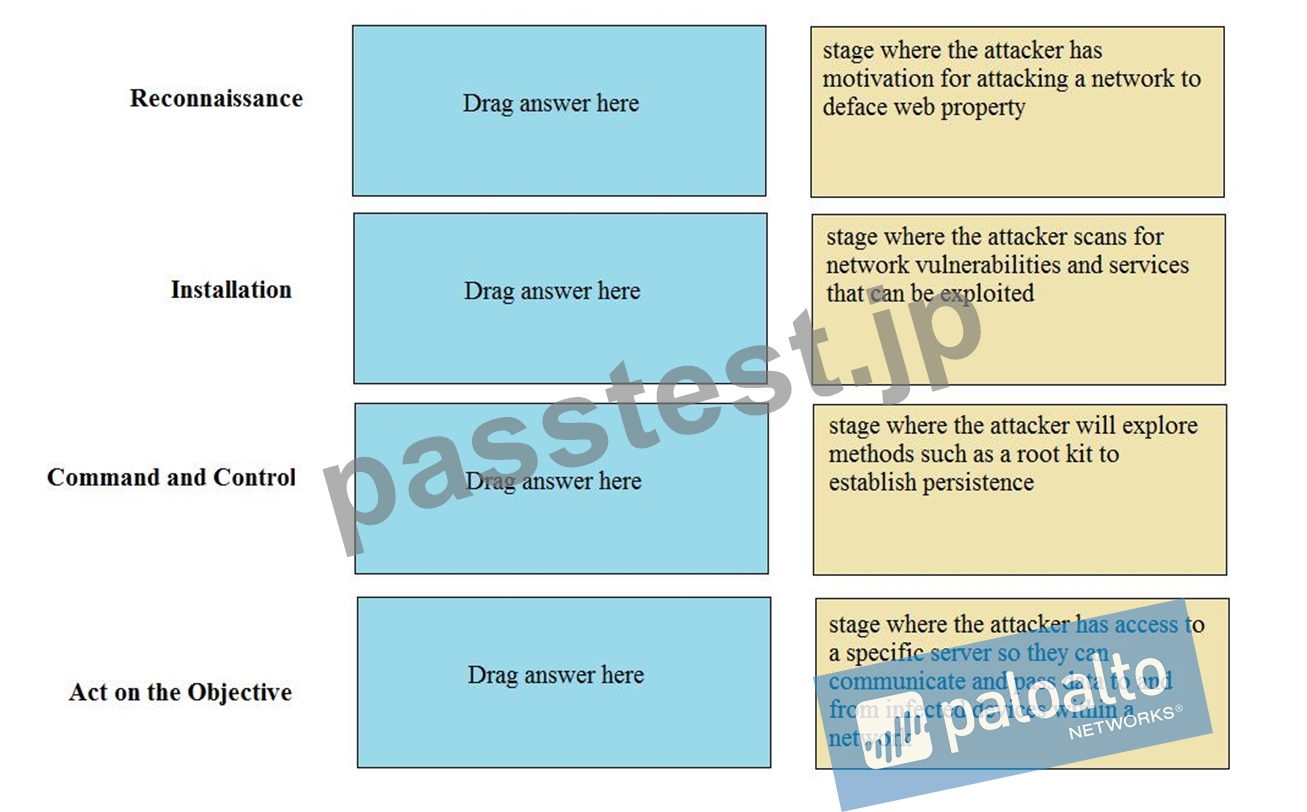
正解:
解説: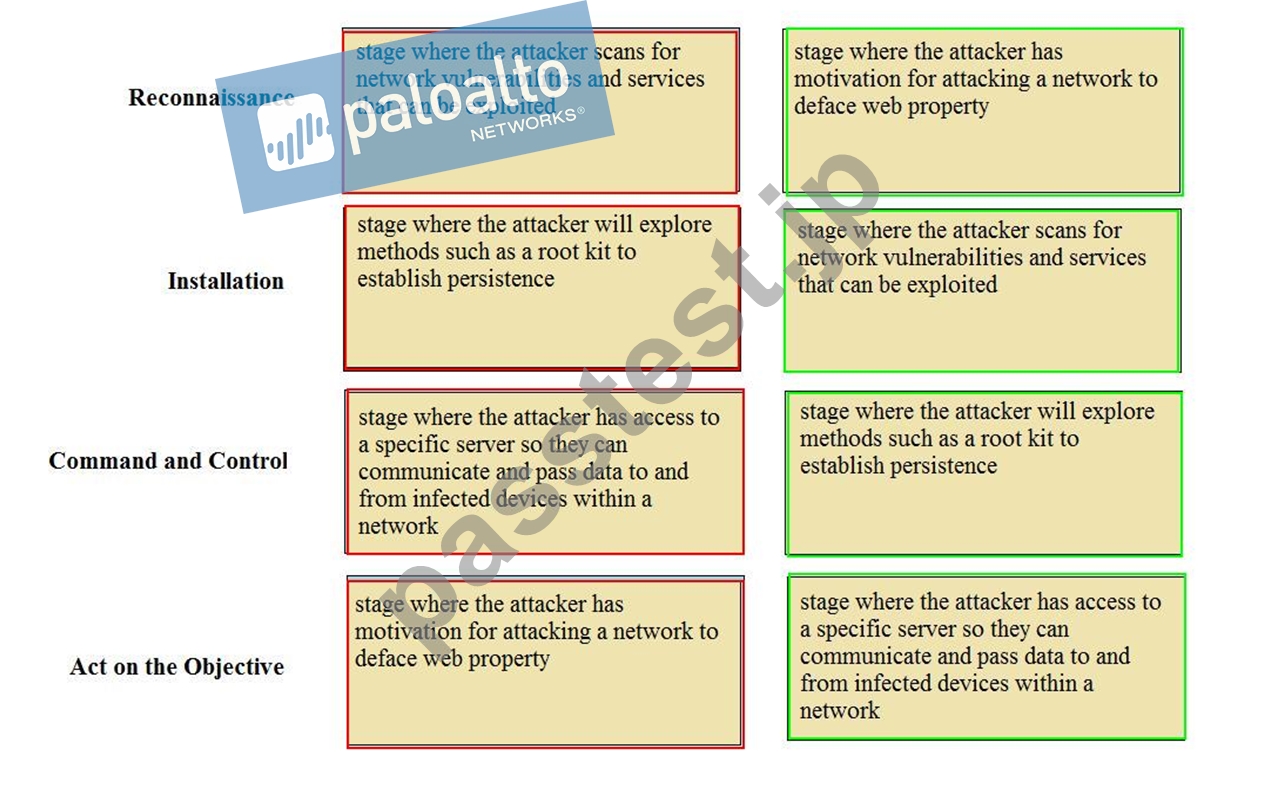
Explanation:
Reconnaissance - stage where the attacker scans for network vulnerabilities and services that can be exploited.
Installation - stage where the attacker will explore methods such as a root kit to establish persistence Command and Control - stage where the attacker has access to a specific server so they can communicate and pass data to and from infected devices within a network.
Act on the Objective - stage where an attacker has motivation for attacking a network to deface web property
質問 # 175
スパイウェア対策プロファイル内の 2 つの有効な選択は何ですか? (2つお選びください。)
- A. ドロップ
- B. 拒否
- C. ランダム早期ドロップ
- D. デフォルト
正解:A、D
質問 # 176
このステートメントを正しく完成させるオプションを選択してください。セキュリティ プロファイルは、トラフィック ____________ をブロックまたは許可できます。
- A. トラフィックを許可またはブロックするセキュリティ ポリシー ルールと一致した後。
- B. データ プレースまたは管理プレーンのいずれか。
- C. トラフィックを許可するセキュリティ ポリシー ルールと一致した後。
- D. セキュリティ ポリシー ルールに一致する前。
正解:C
解説:
Explanation/Reference:
Reference:
https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-admin/policy/security-policy.html After a packet has been allowed by the Security policy, Security Profiles are used to scan packets for threats, vulnerabilities, viruses, spyware, malicious URLs, data exfiltration, and exploitation software.
質問 # 177
管理者アカウントの作成時に管理者が表示および変更できるものを決定するためのより詳細なオプションを提供する管理者タイプはどれですか。
- A. 動的
- B. ルート
- C. スーパーユーザー
- D. ロールベース
正解:D
質問 # 178
システムログとして記録されるのはどのような状況ですか?
- A. なりすまし Web サイトへのアクセスの試みはブロックされました。
- B. 認証サーバーとの接続が切断されました。
- C. 新しい資産がネットワーク上で検出されました。
- D. 分析されたファイルはシステムにとって潜在的に危険です。
正解:B
質問 # 179
......
あなたを合格させるPaloalto Network Security Administrator PCNSA日本語試験問題集で2024年03月23日には361問あります:https://www.passtest.jp/Palo-Alto-Networks/PCNSA-JPN-shiken.html