

2025年05月実際に出るPAM-DEF試験問題集には正確で更新された問題
PAM-DEF試験問題集でPDF問題とテストエンジン
質問 # 130
Which of the following are secure options for storing the contents of the Operator CD, while still allowing the contents to be accessible upon a planned Vault restart? (Choose three.)
- A. Store the server key in a Hardware Security Module (HSM) and copy the rest the keys from the CD to a folder on the Vault Server and secure it with NTFS permissions
- B. Store the CD in a physical safe and mount the CD every time Vault maintenance is performed
- C. Copy the entire contents of the CD to a folder on the Vault Server and secure it with NTFS permissions
- D. Copy the entire contents of the CD to the system Safe on the Vault
正解:A、B、D
解説:
Explanation
* A. Store the CD in a physical safe and mount the CD every time Vault maintenance is performed.
This option ensures that the CD is kept in a secure location when not in use, and that the keys are available when needed. This is the default option suggested by CyberArk1.
* B. Copy the entire contents of the CD to the system Safe on the Vault. This option allows the Vault to access the keys from the system Safe, which is a special Safe that stores the Vault configuration files and keys. The system Safe is encrypted and protected by the Vault, and can only be accessed by authorized users2.
* D. Store the server key in a Hardware Security Module (HSM) and copy the rest the keys from the CD to a folder on the Vault Server and secure it with NTFS permissions. This option provides an additional layer of security for the server key, which is the most critical key for the Vault. An HSM is a physical device that stores and manages cryptographic keys in a tamper-resistant and isolated environment. The Vault can integrate with an HSM to store and retrieve the server key3. The rest of the keys can be stored in a folder on the Vault Server and secured with NTFS permissions, which restrict access to authorized users and groups.
The following option is not secure and should be avoided:
* C. Copy the entire contents of the CD to a folder on the Vault Server and secure it with NTFS permissions. This option exposes the keys to potential risks, such as unauthorized access, data corruption, or deletion. NTFS permissions are not sufficient to protect the keys from malicious or accidental actions. Moreover, this option does not comply with the CyberArk best practices, which recommend to store the keys on a removable media or an HSM
質問 # 131
Which Cyber Are components or products can be used to discover Windows Services or Scheduled Tasks that use privileged accounts? Select all that apply.
- A. On Demand Privileges Manager (OPM)
- B. Discovery and Audit (DMA)
- C. Accounts Discovery
- D. Auto Detection (AD)
- E. Export Vault Data (EVD)
正解:B、C、D
質問 # 132
Which combination of Safe member permissions will allow end users to log in to a remote machine transparently but NOT show or copy the password?
- A. Use Accounts, Retrieve Accounts, List Accounts
- B. Use Accounts, List Accounts
- C. Use Accounts
- D. List Accounts, Retrieve Accounts
正解:D
質問 # 133
The Password upload utility can be used to create safes.
- A. TRUE
- B. FALSE
正解:A
解説:
Explanation
The Password Upload utility can be used to create safes, as well as password objects, folders, and platforms.
The Password Upload utility works with the CyberArk Password Vault to create password objects from a passwords list and store them in the Vault. This enables you to upload large numbers of passwords automatically and makes the Vault implementation process quicker and more automatic. The Password Upload utility initiates the Vault environment required to store passwords in the safe and start working with them. This includes creating new safes, adding the CPM user as a safe owner, and sharing the safe with the Password Vault Web Access1. References:
* 1: Password Upload Utility
質問 # 134
You are creating a shared safe for the help desk.
What must be considered regarding the naming convention?
- A. The use of these characters V:*<>".| is not allowed.
- B. Ensure your naming convention is no longer than 20 characters.
- C. Combine environments, owners and platforms to minimize the total number of safes created.
- D. Safe owners should determine the safe name to enable them to easily remember it.
正解:A
解説:
Explanation
When creating a shared safe for the help desk in CyberArk's Privileged Access Management (PAM), it is important to adhere to the naming conventions set forth by CyberArk. One of the key considerations is that certain characters are not permitted in the safe name. Specifically, the characters V:*<>".| are not allowed in the naming of safes. This is to ensure compatibility and prevent issues with the file system or the CyberArk application itself, as these characters may interfere with normal operations or be reserved for specific functions within the operating system or the application.
References: The information regarding safe naming conventions is based on CyberArk's best practices and guidelines, which are detailed in the official CyberArk documentation and study guides. It is important to consult the CyberArk Defender PAM resources and documents to ensure compliance with these standards
質問 # 135
Before failing back to the production infrastructure after a DR exercise, what must you do to maintain audit history during the DR event?
- A. Ensure that the Production Instance replicates changes that occurred from the Disaster Recovery Instance.
- B. Stop the CPM services before starting the production server.
- C. Briefly stop and start the Disaster Recovery Instance before attempting to fail components back to the Production Instance.
- D. Perform an IIS Reset on all PVWA servers.
正解:A
解説:
Explanation
Before failing back to the production infrastructure after a Disaster Recovery (DR) exercise, it is crucial to ensure that the Production Instance replicates all changes that occurred from the Disaster Recovery Instance.
This includes all audit history and any other changes made during the DR event. The replication process ensures that no data is lost and that the audit history is maintained consistently across both the DR and Production environments1.
References:
* CyberArk Docs - Reports and Audits1
* CyberArk Docs - Vault Audit Action Codes2
* CyberArk Blog - Failover and Failback Process
質問 # 136
For each listed prerequisite, identify if it is mandatory or not mandatory to run the PSM Health Check.
正解:
解説:

質問 # 137
If a user is a member of more than one group that has authorizations on a safe, by default that user is granted________.
- A. only those permissions that exist in all groups to which the user belongs.
- B. the vault will not allow this situation to occur.
- C. the cumulative permissions of all groups to which that user belongs.
- D. only those permissions that exist on the group added to the safe first.
正解:D
質問 # 138
ADR Vault became active due to a failure of the primary Vault. Service on the primary Vault has now been restored. Arrange the steps to return the DR vault to its normal standby mode in the correct sequence.
正解:
解説:
Explanation
* Shut down the PrivateArk Server Service on the DR Vault.
* In the PADR.ini file, set Failover Mode = No and remove the last two lines.
* Start the PrivateArk Disaster Recovery Service.
Comprehensive Explanation: When the primary Vault service has been restored and you need to return the DR Vault to its normal standby mode, the steps are as follows:
* Shut down the PrivateArk Server Service on the DR Vault to stop the Vault from being active.
* Modify the PADR.ini file by setting Failover Mode to No and removing the last two lines that were added during the failover process. This reconfigures the DR Vault to standby mode.
* Start the PrivateArk Disaster Recovery Service to complete the transition back to standby mode1.
References:
* CyberArk Docs - Initiate a DR Failback to the Production Vault1
質問 # 139
Arrange the steps to restore a Vault using PARestore for a Backup in the correct sequence.
正解:
解説:
Explanation
BackupFilesDeletion=No
PARestore vault.ini operator /FullVaultRestore
CAVaultManager RecoverBackupFiles
CAVaultManager RestoreDB
BackupFilesDeletion=Yes,24,1,5,7d
https://docs.cyberark.com/Product-Doc/OnlineHelp/PAS/Latest/en/Content/PASIMP/Restoring-Safes-or-the-Vau
質問 # 140
CyberArk implements license limits by controlling the number and types of users that can be provisioned in the vault.
- A. TRUE
- B. FALSE
正解:A
質問 # 141
An auditor initiates a live monitoring session to PSM server to view an ongoing live session. When the auditor's machine makes an RDP connection the PSM server, which user will be used?
- A. PSMConnect
- B. Credentials stored in the Vault for the target machine
- C. Shadowuser
- D. PSMAdminConnect
正解:D
解説:
Explanation
According to the web search results, when an auditor initiates a live monitoring session to PSM server to view an ongoing live session, the auditor's machine makes an RDP connection to the PSM server using the PSMAdminConnect user. The PSMAdminConnect user is a local or domain user that starts PSM sessions on the PSM machine for authorized users who want to monitor or terminate active sessions1. The PSMAdminConnect user has limited permissions and access rights on the PSM server, and its credentials are managed by the CPM. The PSMAdminConnect user retrieves the credentials of the target account from the vault and uses them to establish a secure connection to the target machine. The auditor can then view the live session through the PSM session, while the PSM server records and audits the session activity.
質問 # 142
Time of day or day of week restrictions on when password verifications can occur configured in
____________________.
- A. The Master Policy
- B. The Account Details
- C. The Platform settings
- D. The Safe settings
正解:C
質問 # 143
It is possible to restrict the time of day, or day of week that a [b]verify[/b] process can occur
- A. TRUE
- B. FALSE
正解:A
解説:
Explanation
It is possible to restrict the time of day, or day of week that a verify process can occur by using the Verify Time Window parameter in the Platform Management page. This parameter allows the administrator to define a time window for each platform, during which the verify process can be performed. The verify process will not run outside of this time window, unless it is manually initiated by the administrator. This feature can help reduce the load on the target systems and the network during peak hours. References:
* [Defender PAM Course], Module 4: Managing Accounts, Lesson 2: Account Verification, Slide 8:
Verify Time Window
* [Defender PAM Documentation], Version 12.3, Administration Guide, Chapter 4: Managing Platforms, Section: Verify Time Window
質問 # 144
Which dependent accounts does the CPM support out-of-the-box? (Choose three.)
- A. Windows Scheduled
- B. Solaris Configuration file
- C. Windows DCOM Applications
- D. Windows Services
- E. Key Tab file
- F. Windows Registry
正解:A、D、F
解説:
Explanation
Dependent accounts are accounts that represent resources such as Windows Services, Windows Scheduled Tasks, and others, which are accessed from a target machine and require the same credentials as the target machine. The CyberArk Privileged Account Security Solution's Central Policy Manager (CPM) supports out-of-the-box dependent accounts for Windows Services, Windows Scheduled Tasks, and Windows Registry.
When changing a password, the CPM synchronizes the target account password with all other occurrences of that password in any related dependent accounts. This ensures that all dependent accounts are updated simultaneously to maintain security and functionality12. References:
* CyberArk Docs: Manage dependent accounts1
* CyberArk Docs: Supported dependent accounts
質問 # 145
If a user is a member of more than one group that has authorizations on a safe, by default that user is granted________.
- A. the cumulative permissions of all groups to which that user belongs.
- B. only those permissions that exist on the group added to the safe first.
- C. only those permissions that exist in all groups to which the user belongs.
- D. the vault will not allow this situation to occur.
正解:A
解説:
Explanation
When a user is a member of more than one group that has authorizations on a safe, by default that user is granted the cumulative permissions of all groups to which that user belongs. This means that the user will have the highest level of access that any of the groups have on the safe. For example, if one group has View and Retrieve permissions, and another group has Add and Delete permissions, the user will have View, Retrieve, Add, and Delete permissions on the safe. This is the default behavior of the vault, unless the Exclusive option is enabled on the safe. The Exclusive option restricts the user's permissions to only those of the group added to the safe first. References:
* [Defender PAM eLearning Course], Module 3: Safes and Permissions, Lesson 3.2: Safe Permissions, Slide 8: Cumulative Permissions
* [Defender PAM Sample Items Study Guide], Question 1: Safe Permissions
* [CyberArk Documentation Portal], CyberArk Privileged Access Security Implementation Guide, Chapter 3: Managing Safes, Section: Safe Properties, Subsection: Exclusive
質問 # 146
How much disk space do you need on a server to run a full replication with PAReplicate?
- A. same as disk size on Satellite Vault
- B. 500 GB
- C. at least the same disk size as the Primary Vault
- D. 1 TB
正解:C
質問 # 147
Which type of automatic remediation can be performed by the PTA in case of a suspected credential theft security event?
- A. Session suspension
- B. Password reconciliation
- C. Session termination
- D. Password change
正解:D
解説:
Explanation
The PTA can perform automatic password change as a type of remediation in case of a suspected credential theft security event. According to the CyberArk documentation1, "Rotate credentials - for OverPass the Hash attack and Suspected credentials theft events."1 This means that the PTA can initiate a password change request to the CPM for the affected account, which will generate a new random password and update it on the target system and the Vault. This way, the PTA can prevent the attacker from using the stolen credentials to access the target system or launch further attacks. References:
* Configure PTA Remediations - CyberArk, section "Remediation Initiation"
質問 # 148
If the AccountUploader Utility is used to create accounts with SSH keys, which parameter do you use to set the full or relative path of the SSH private key file that will be attached to the account?
- A. Address
- B. KeyPath
- C. KeyFile
- D. ObjectName
正解:C
解説:
Explanation
When using the AccountUploader Utility to create accounts with SSH keys, the parameter used to set the full or relative path of the SSH private key file that will be attached to the account is KeyFile. This parameter specifies the location of the SSH private key file, which is then associated with the account being onboarded into the CyberArk Privileged Access Security system. The correct configuration of this parameter is crucial for the successful attachment of the SSH key to the account1.
References:
* CyberArk's official documentation on the AccountUploader Utility, which provides detailed information on the parameters and usage for onboarding accounts with SSH keys1.
質問 # 149
One can create exceptions to the Master Policy based on ____________________.
- A. Accounts
- B. Safes
- C. Policies
- D. Platforms
正解:A
質問 # 150
In order to connect to a target device through PSM, the account credentials used for the connection must be stored in the vault?
- A. False. Because if credentials are not stored in the vault, the PSM will log into the target device as PSM Connect.
- B. False. Because the user can also enter credentials manually using Secure Connect.
- C. False. Because if credentials are not stored in the vault, the PSM will prompt for credentials.
- D. True.
正解:B
解説:
Explanation
In order to connect to a target device through PSM, the account credentials used for the connection do not necessarily have to be stored in the vault. The user can also enter credentials manually using Secure Connect, which is a feature that enables users to connect to target systems through PSM without storing the account credentials in the vault. Secure Connect allows users to provide their own credentials at the time of connection, and these credentials are not saved or managed by CyberArk. Secure Connect can be used with any connection component that supports PSM, such as RDP, SSH, WinSCP, etc. To use Secure Connect, the user needs to specify the target system address and the connection component ID in the URL, and then enter the credentials in the PSM login screen1.
The other options are not correct, because:
* A. True. This is not correct, because as explained above, the user can also enter credentials manually using Secure Connect.
* C. False. Because if credentials are not stored in the vault, the PSM will log into the target device as PSM Connect. This is not correct, because PSM Connect is a predefined user that is created on the PSM server during the installation. This user is used to establish the connection between the PSM server and the target server, and to run the PSM processes. The PSM Connect user is not used to log into the target device as the end user2.
* D. False. Because if credentials are not stored in the vault, the PSM will prompt for credentials. This is not correct, because this option is essentially the same as Secure Connect, which is the correct answer.
References:
* 1: Secure Connect
* 2: PSMConnect and PSMAdminConnect
質問 # 151
Which parameter controls how often the CPM looks for Soon-to-be-expired Passwords that need to be changed.
- A. The CPM does not change the password under this circumstance
- B. HeadStartInterval
- C. Interval
- D. ImmediateInterval
正解:B
質問 # 152
Where can PTA be configured to send alerts? (Choose two.)
- A. PAReplicate
- B. Email
- C. EVD
- D. SIEM
- E. Google Analytics
正解:B、D
質問 # 153
DRAG DROP
Match each key to its recommended storage location.
正解:
解説: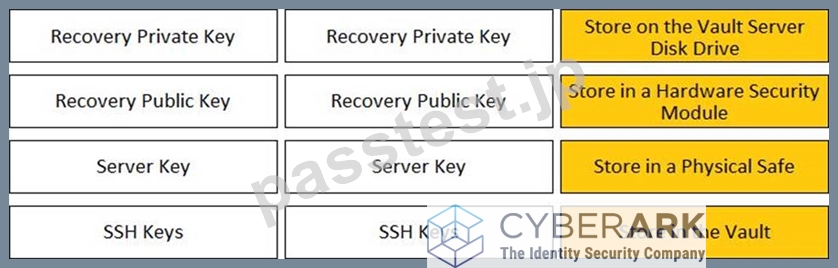
質問 # 154
......
合格させるCyberArk PAM-DEF試験最速合格にはPassTest:https://www.passtest.jp/CyberArk/PAM-DEF-shiken.html
PAM-DEF問題集で必ず試験合格させる:https://drive.google.com/open?id=1-i9YrF0-7yoTHKDTjv0fTHfa_8b5VKYV